Malicious websites today
88,898
Malicious websites this week
890,259
Malicious websites this month
2,330,856
Total malicious websites
21,143,000
TLD distribution
- .com - 50.6%
- .top - 17.1%
- .xyz - 9.9%
- .cc - 6.2%
- .shop - 3.3%
- .buzz - 3.3%
- .net - 3.0%
- .cn - 2.5%
- .org - 2.3%
- .info - 1.8%
Threat trend
19.1M19.8M20.5M21.1M
Threats16/0822/0828/0802/0908/0914/09
Recent threats
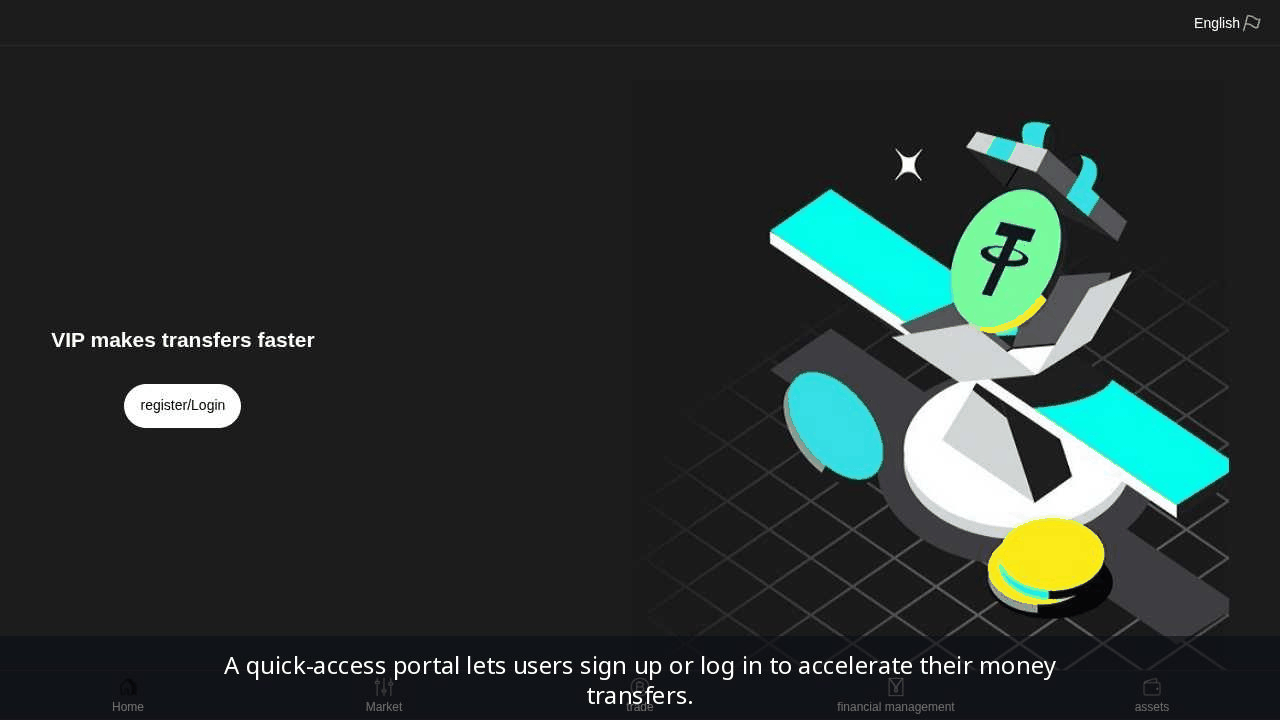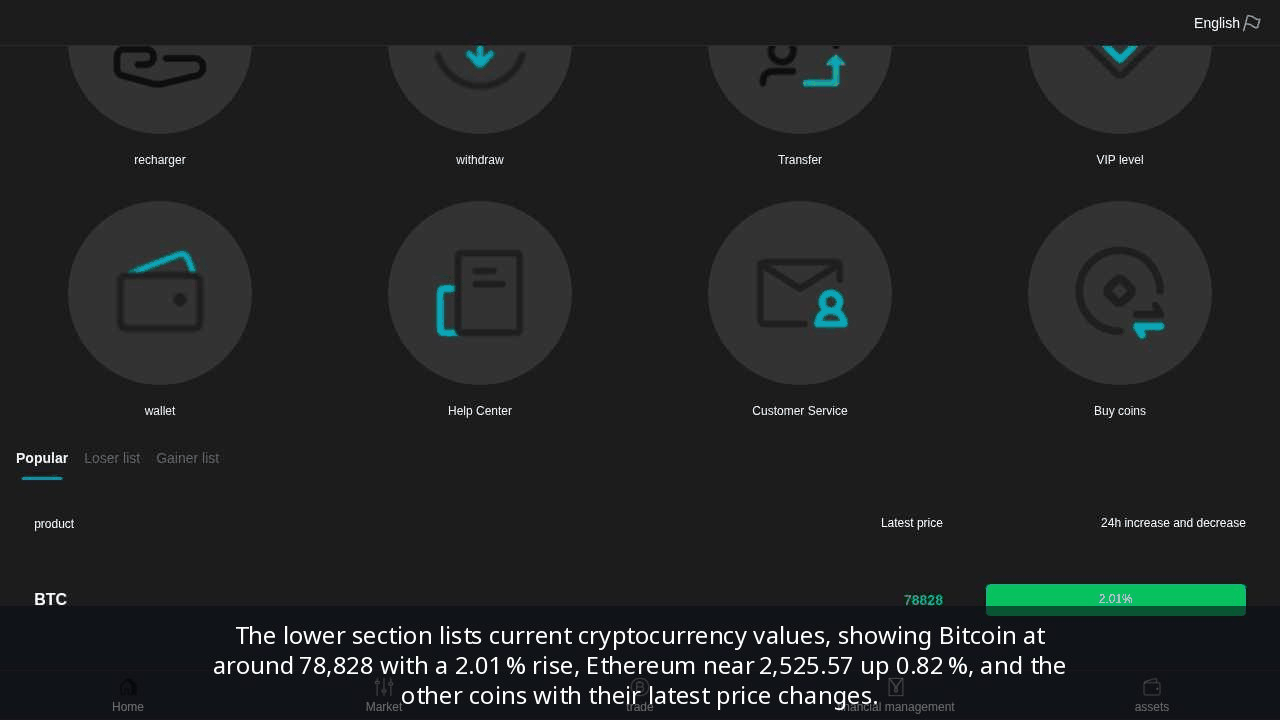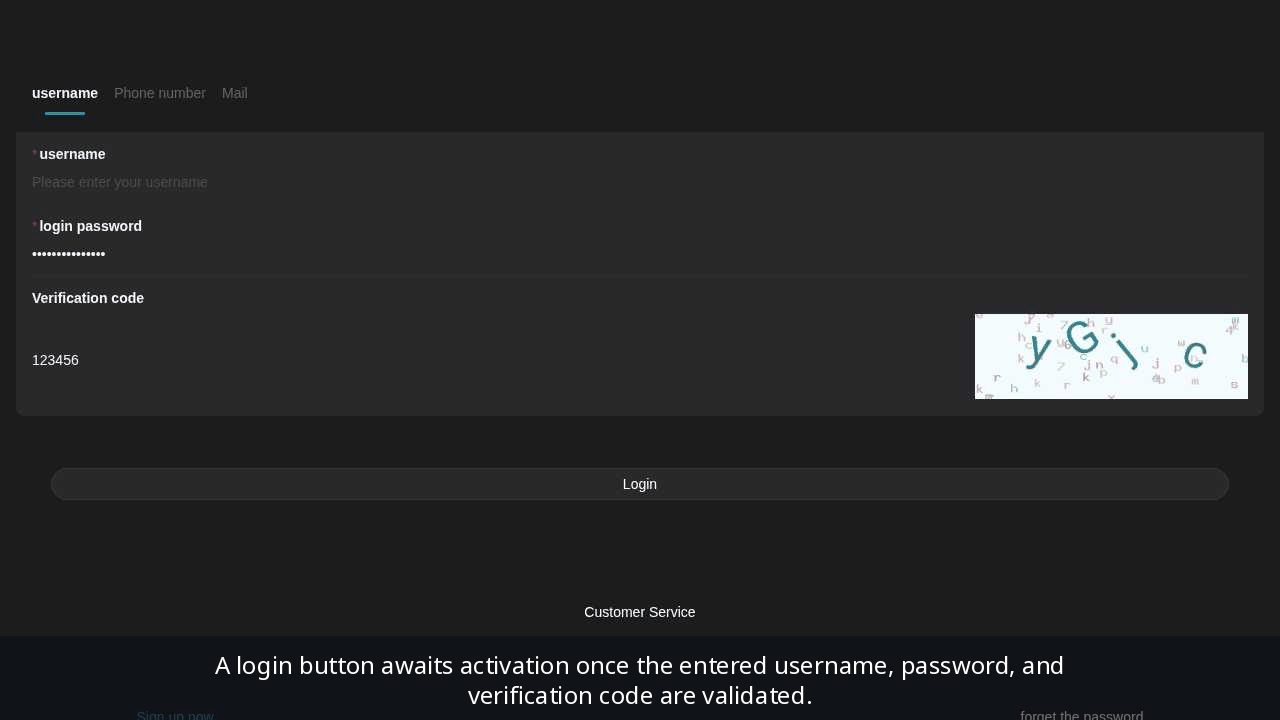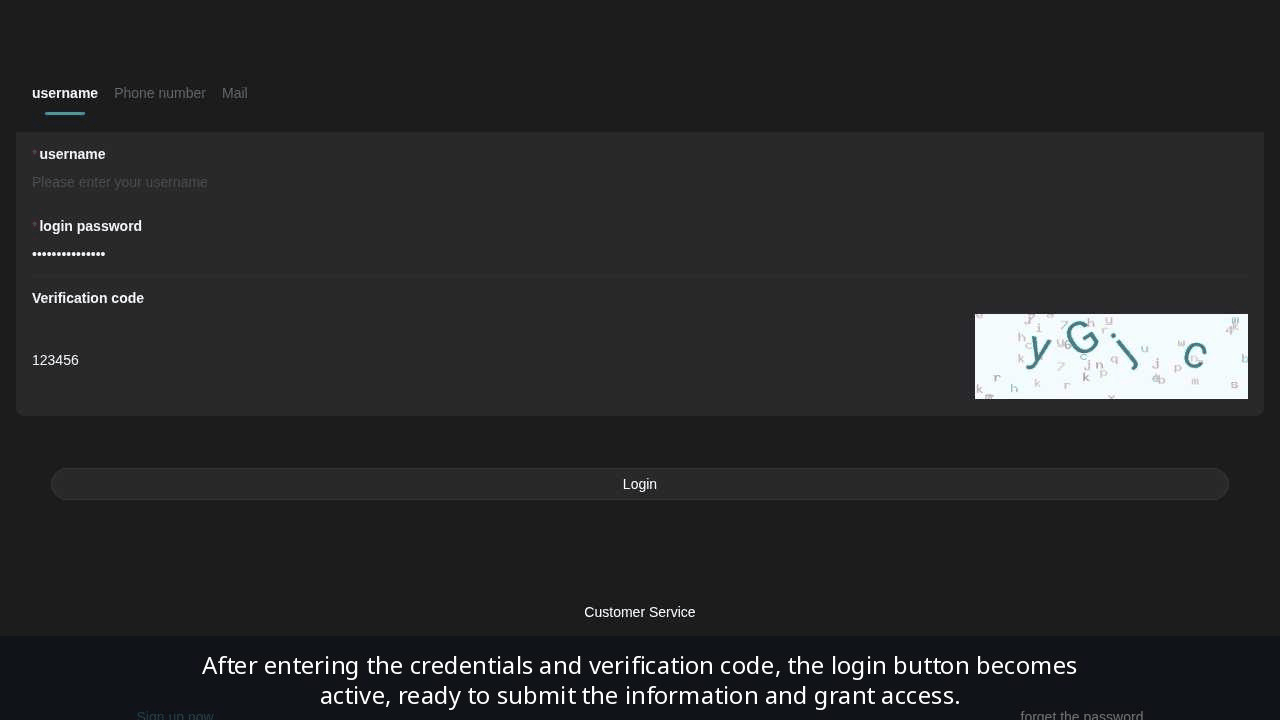
https://us1dt.com
Risk score9/10- The domain us1dt.com was registered very recently, which is a common characteristic of domains used for malicious purposes.
- The registrant is listed as CN, suggesting a Chinese origin, which is frequently associated with phishing or scam operations.
https://redditearn.lovable.app
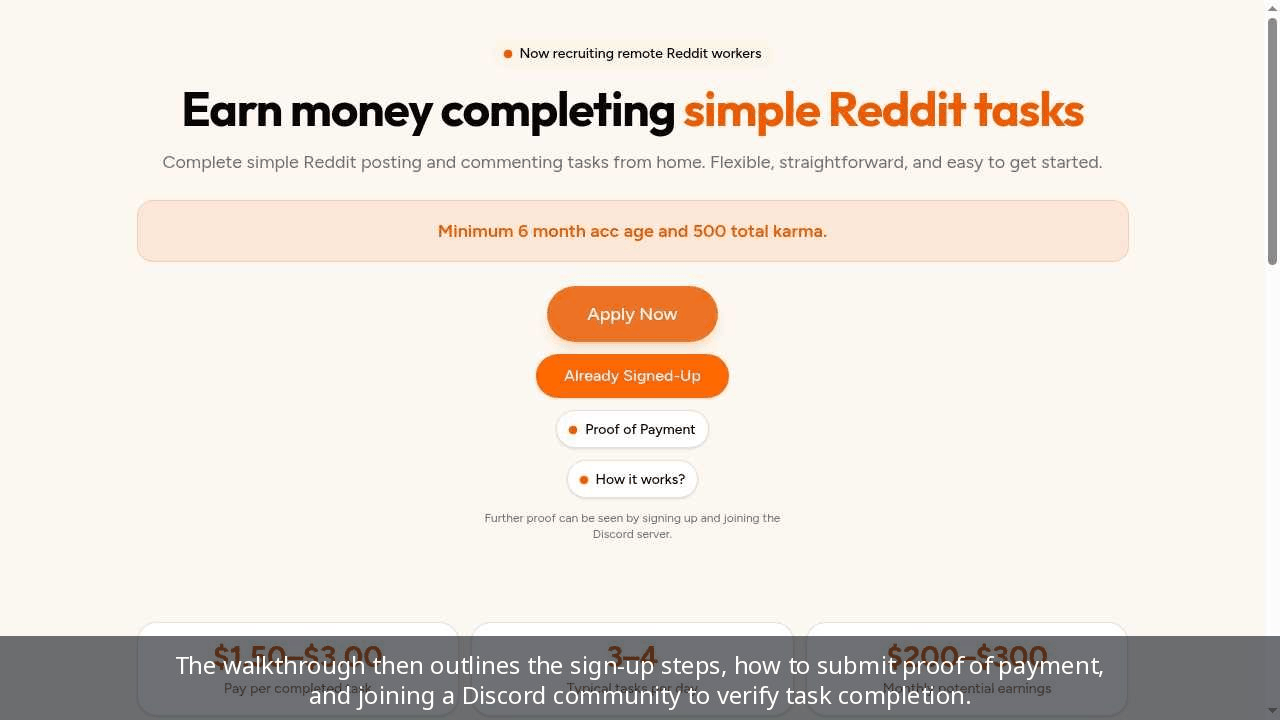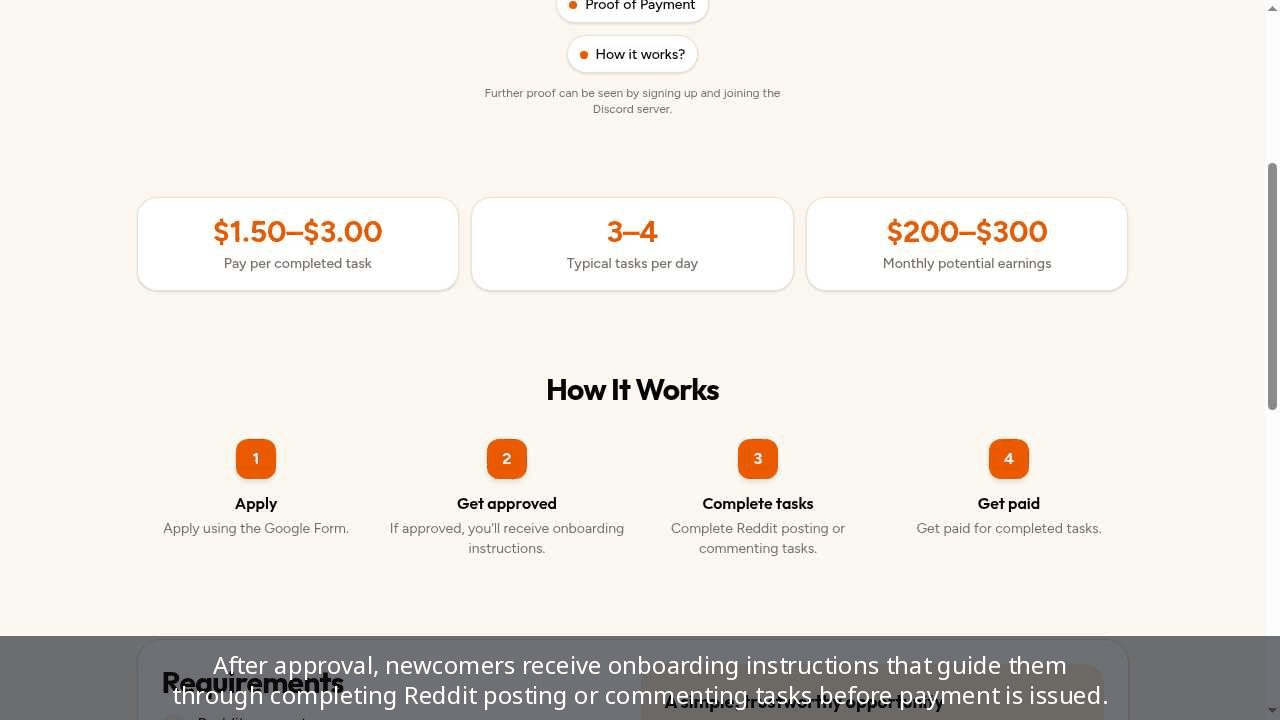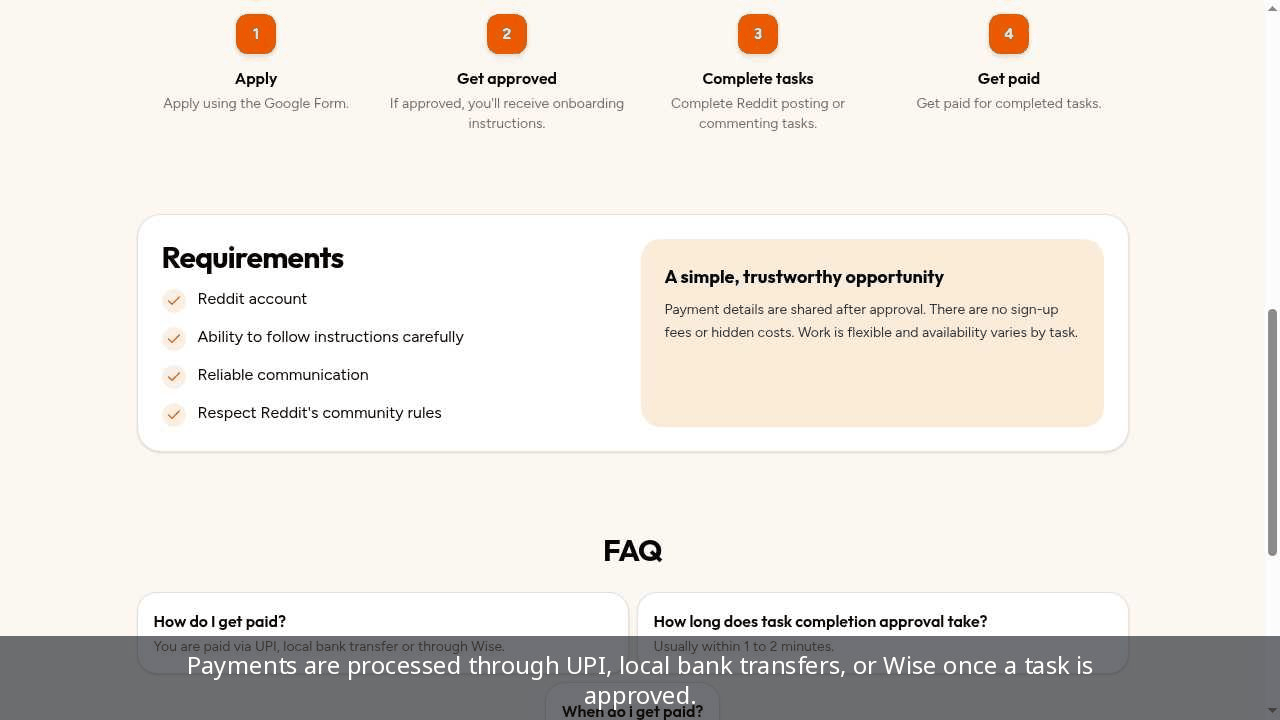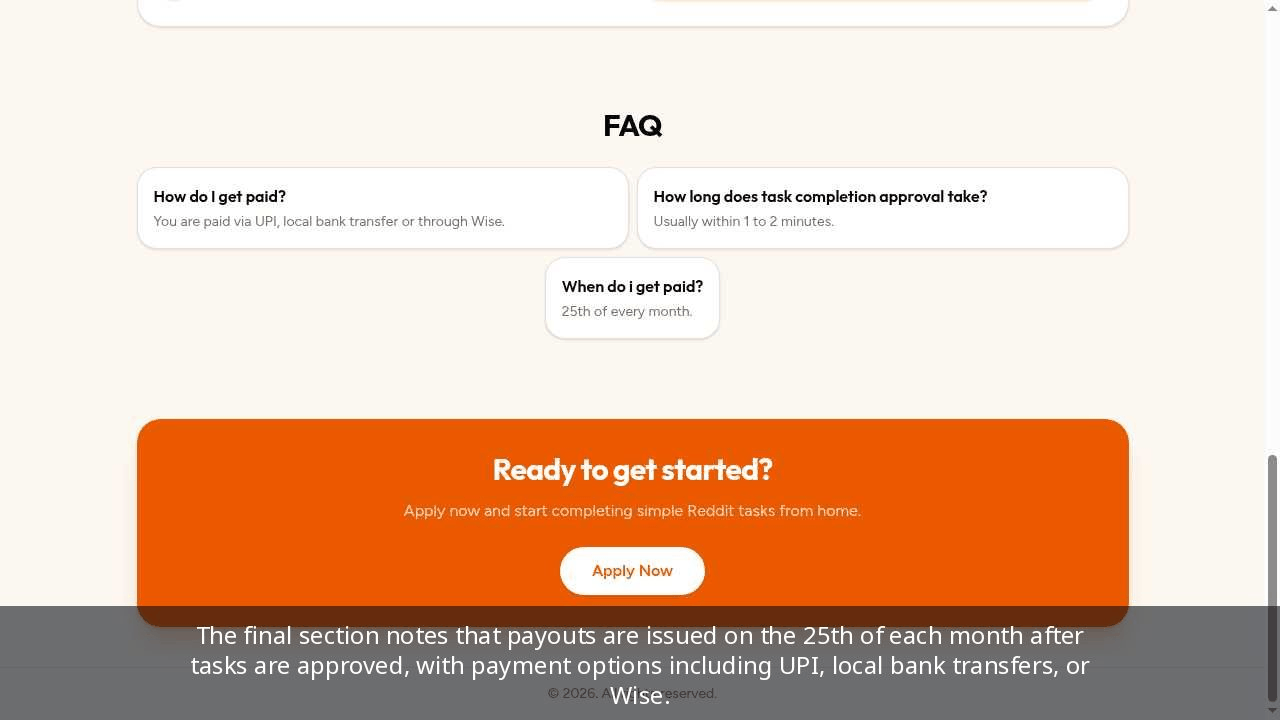
Risk score9/10- The page is hosted on lovable.app, a platform that allows users to quickly create and deploy websites, which is frequently abused by scammers to create low-effort fraudulent pages.
- The site claims to offer paid work for completing simple Reddit tasks such as posting and commenting, a classic structure of a task scam designed to recruit unwitting participants into astroturfing or manipulation campaigns.
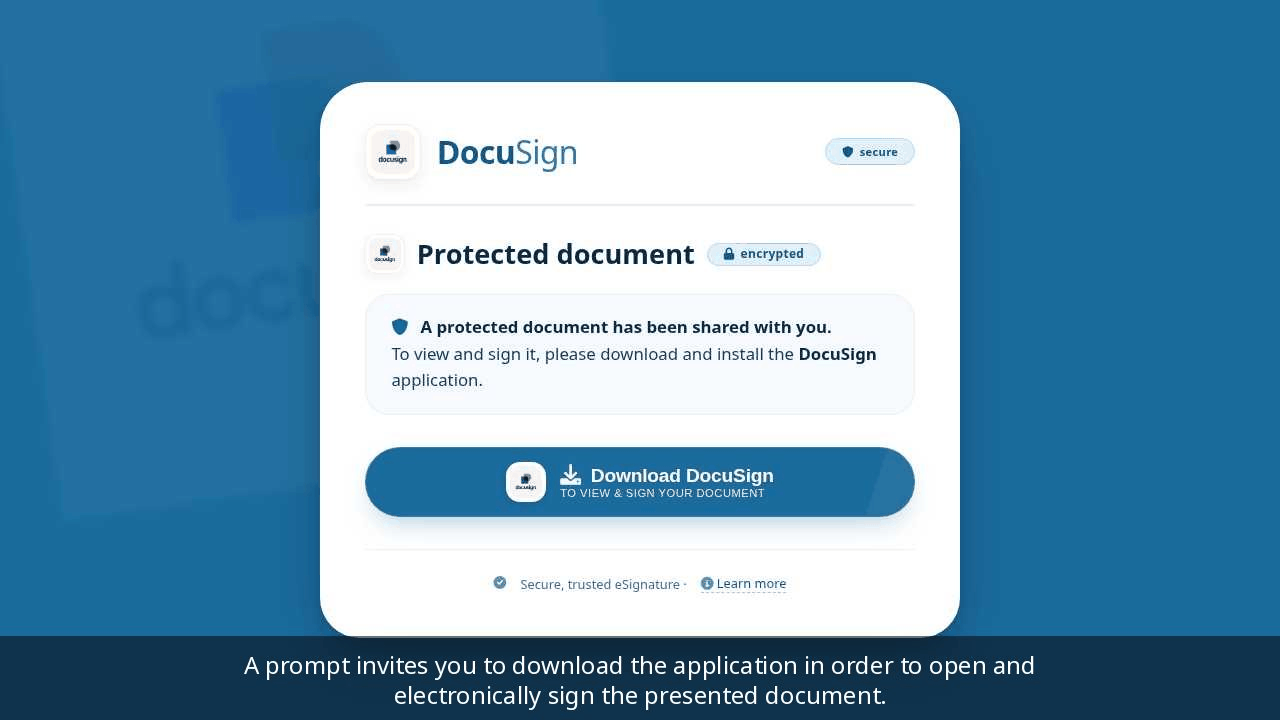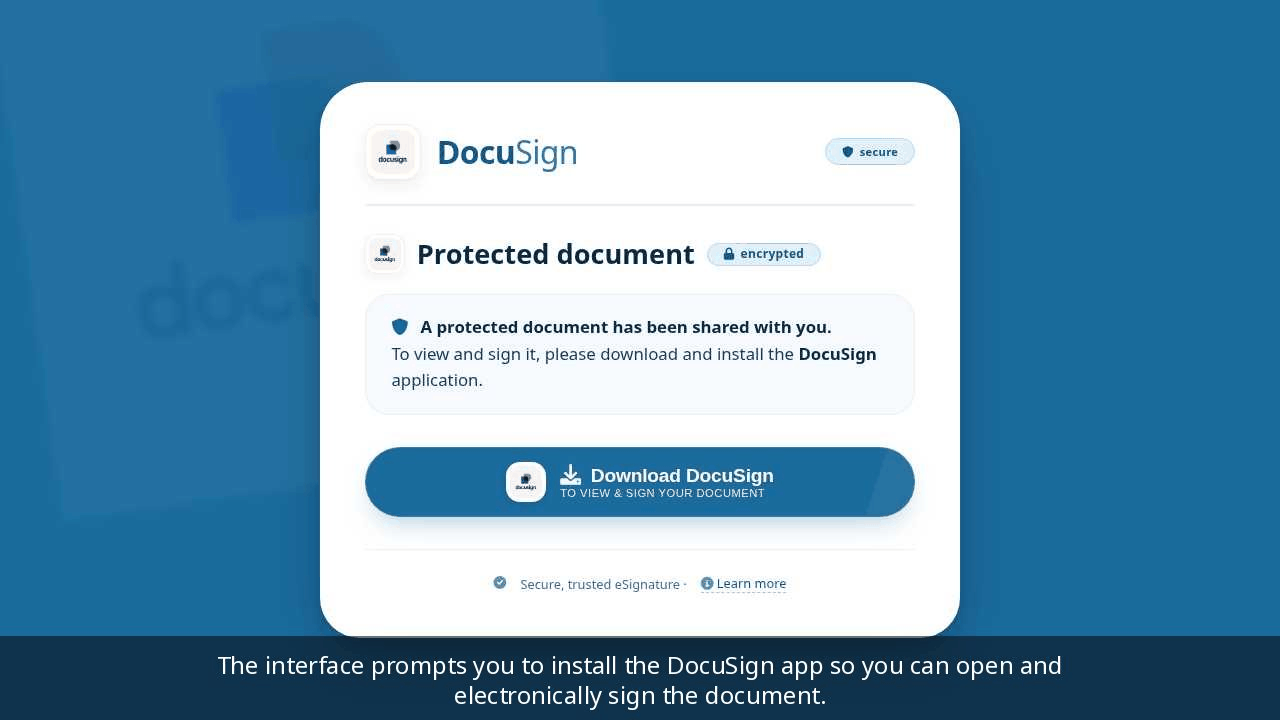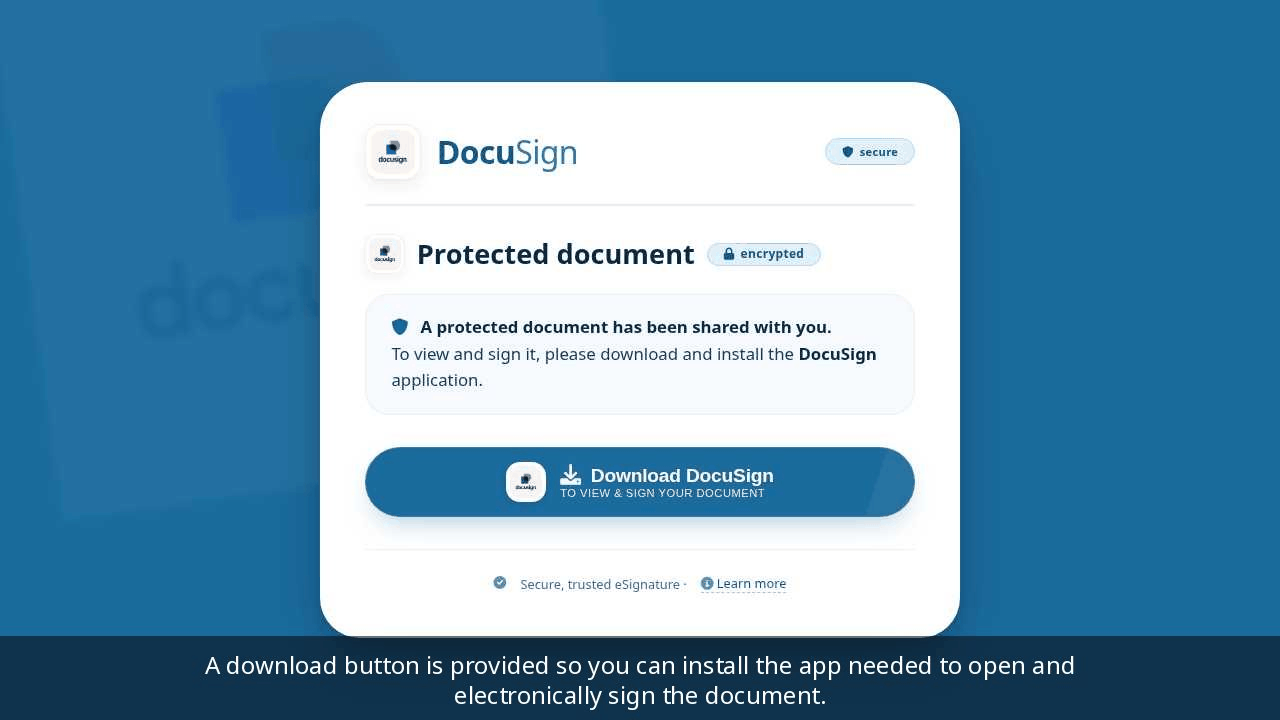
https://docs-sign.live
Risk score10/10- The domain docs-sign.live is not the legitimate DocuSign domain, which is docusign.com, indicating a clear brand impersonation attempt.
- The domain was registered very recently, which is a common characteristic of phishing infrastructure set up for short-lived campaigns.
https://ufg.finance
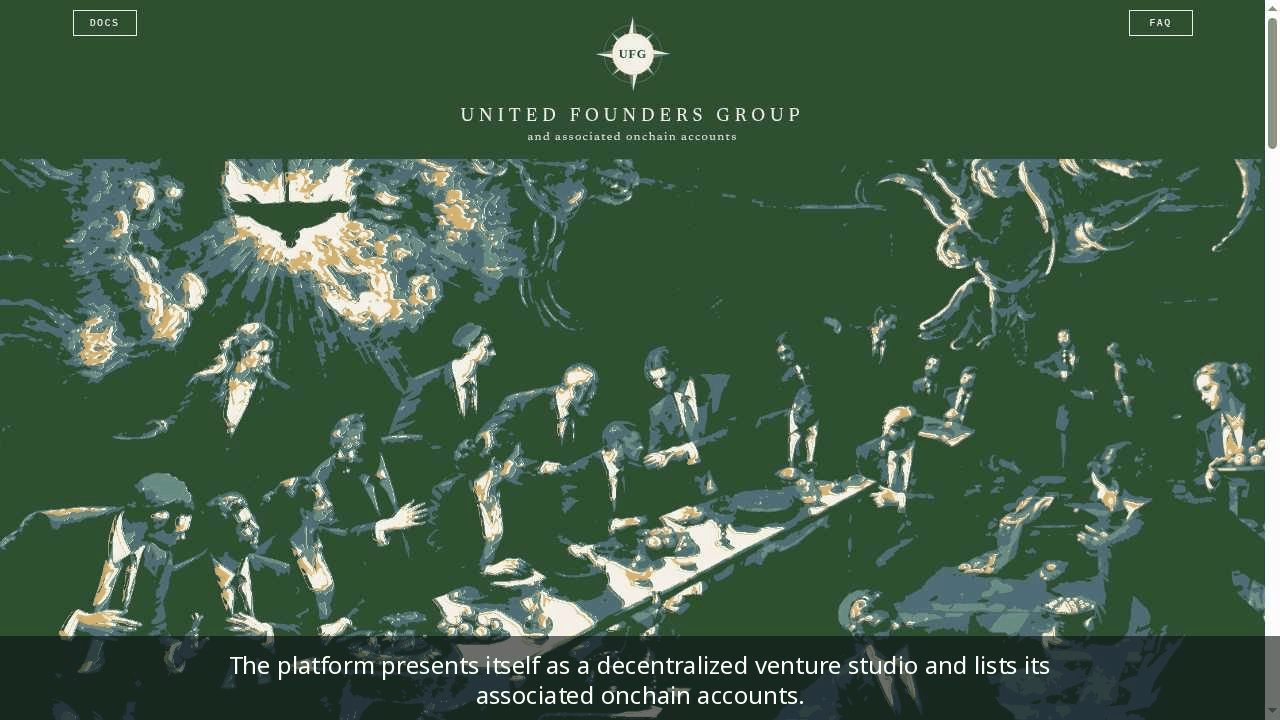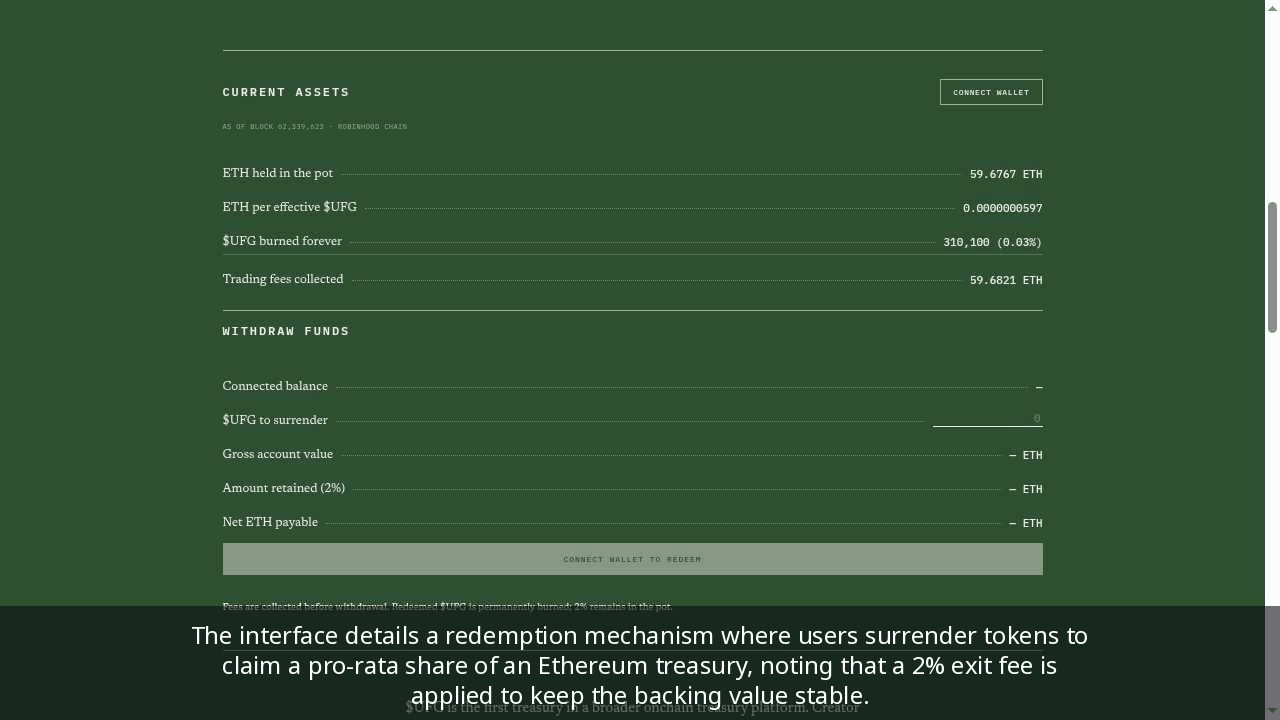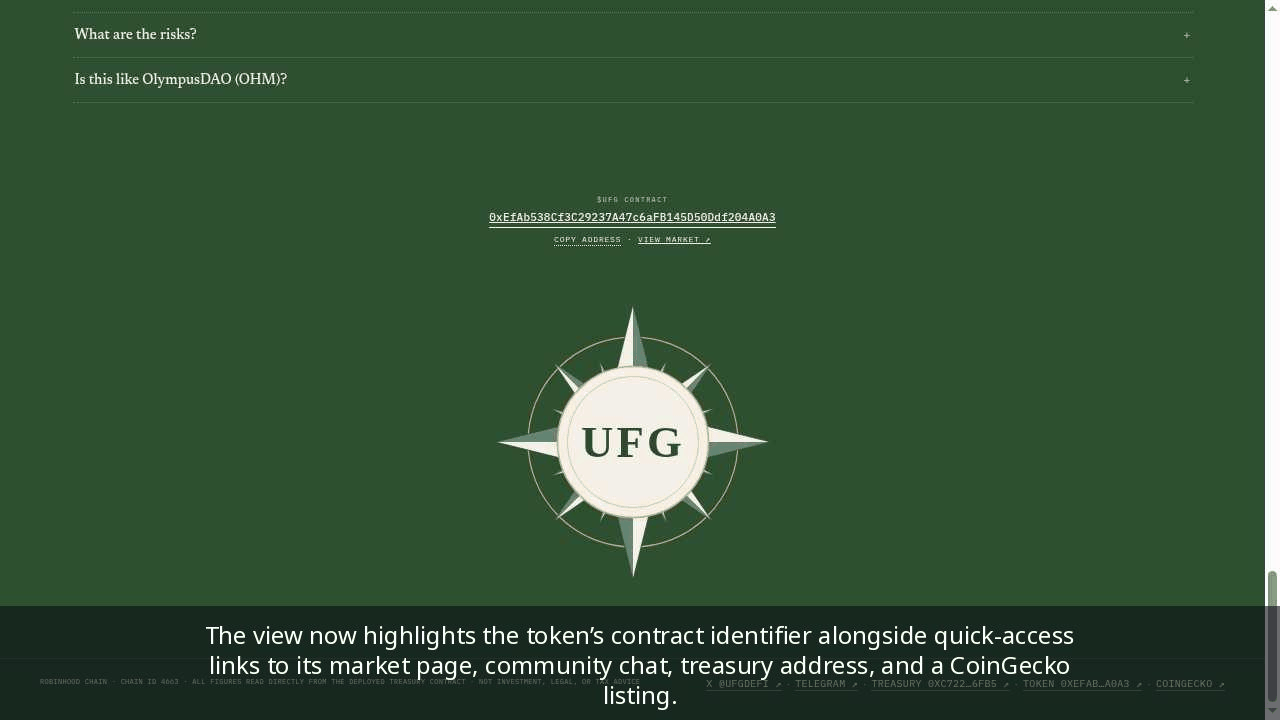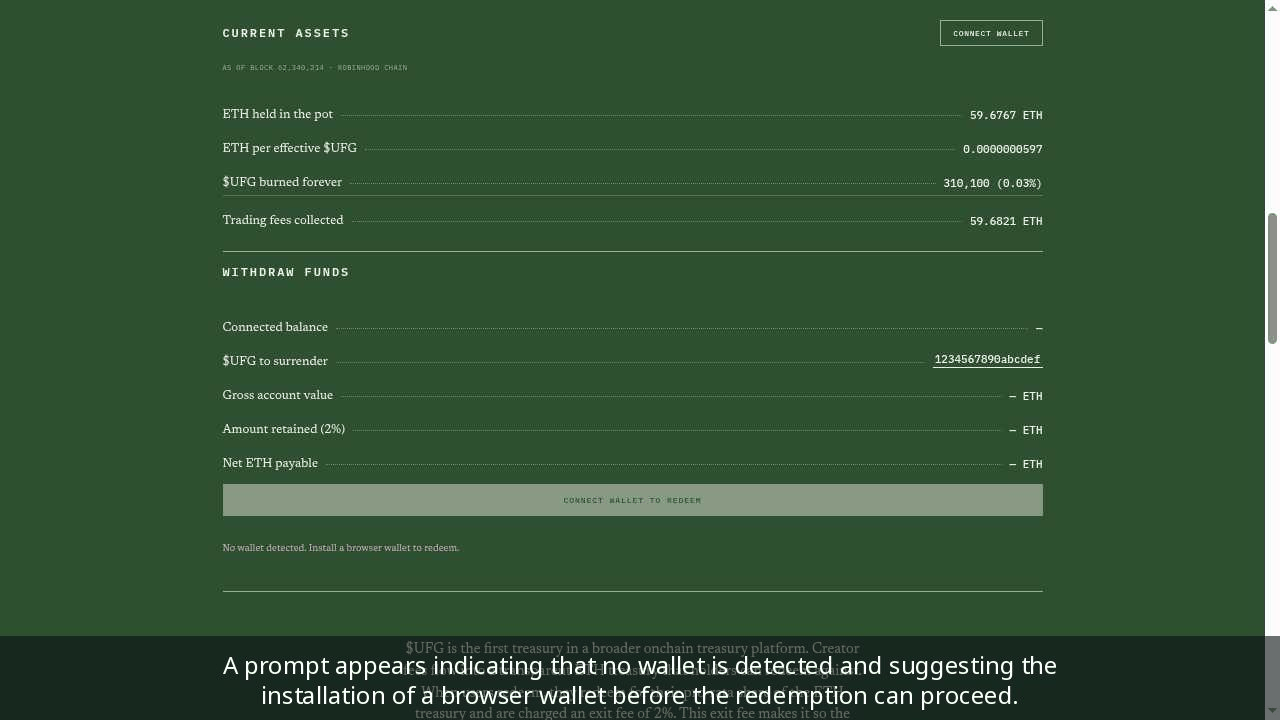
Risk score9/10- The domain ufg.finance was registered very recently on August 30, 2026, only about two weeks before today's date, which is a common pattern for newly created scam or fraudulent sites.
- The site presents itself as a decentralized finance treasury platform offering a token called $UFG with a redemption mechanism, but it explicitly states the contract was not externally audited before launch, which is a significant red flag for a platform handling user funds.
https://liteapks.com/download/fighting-fantas...
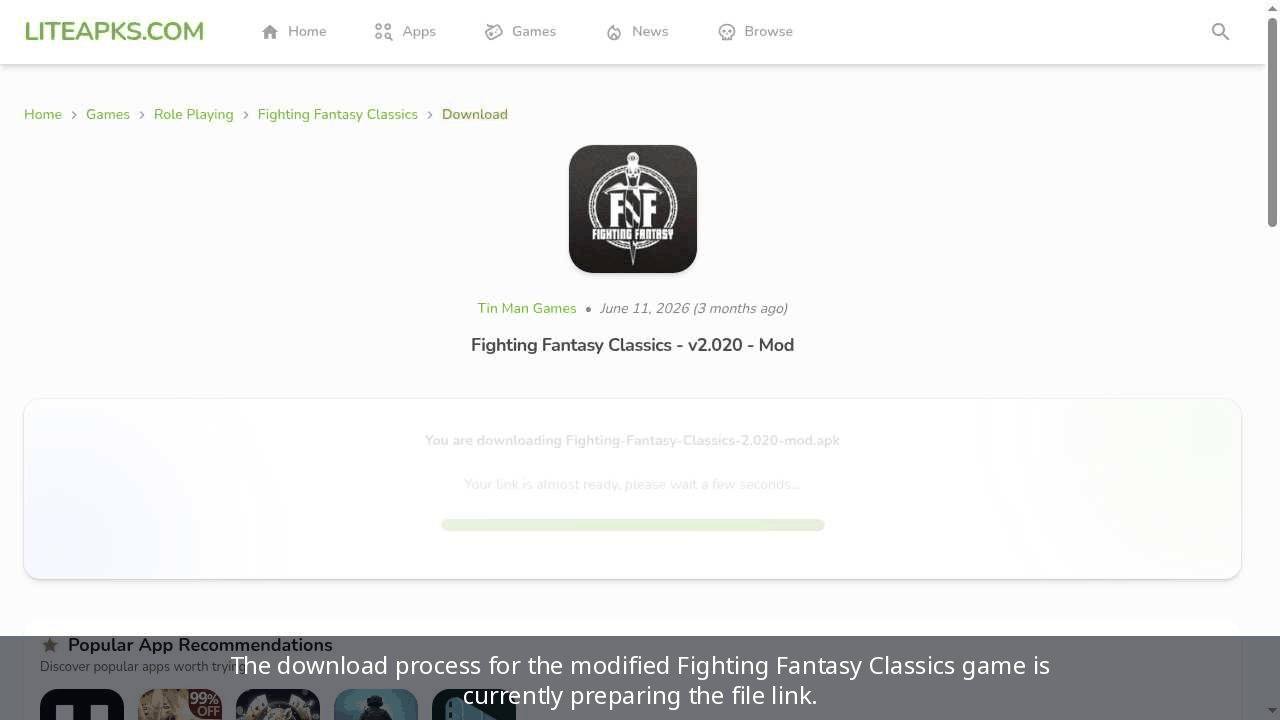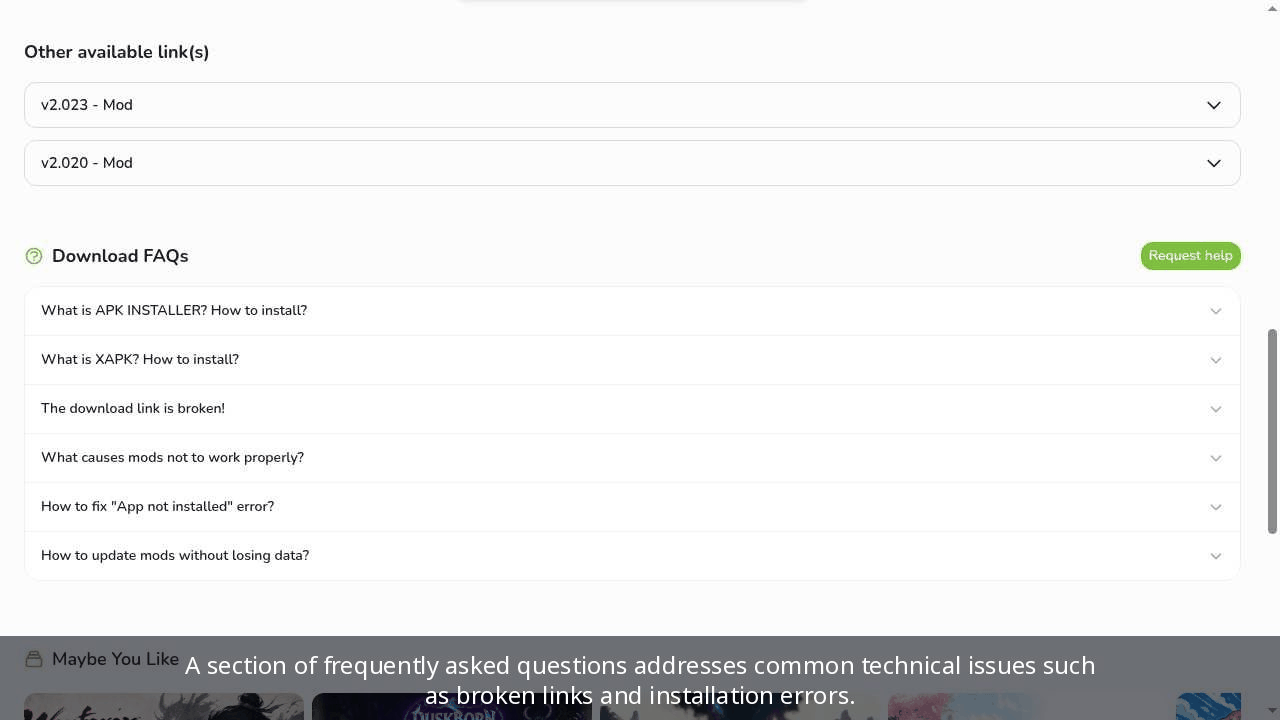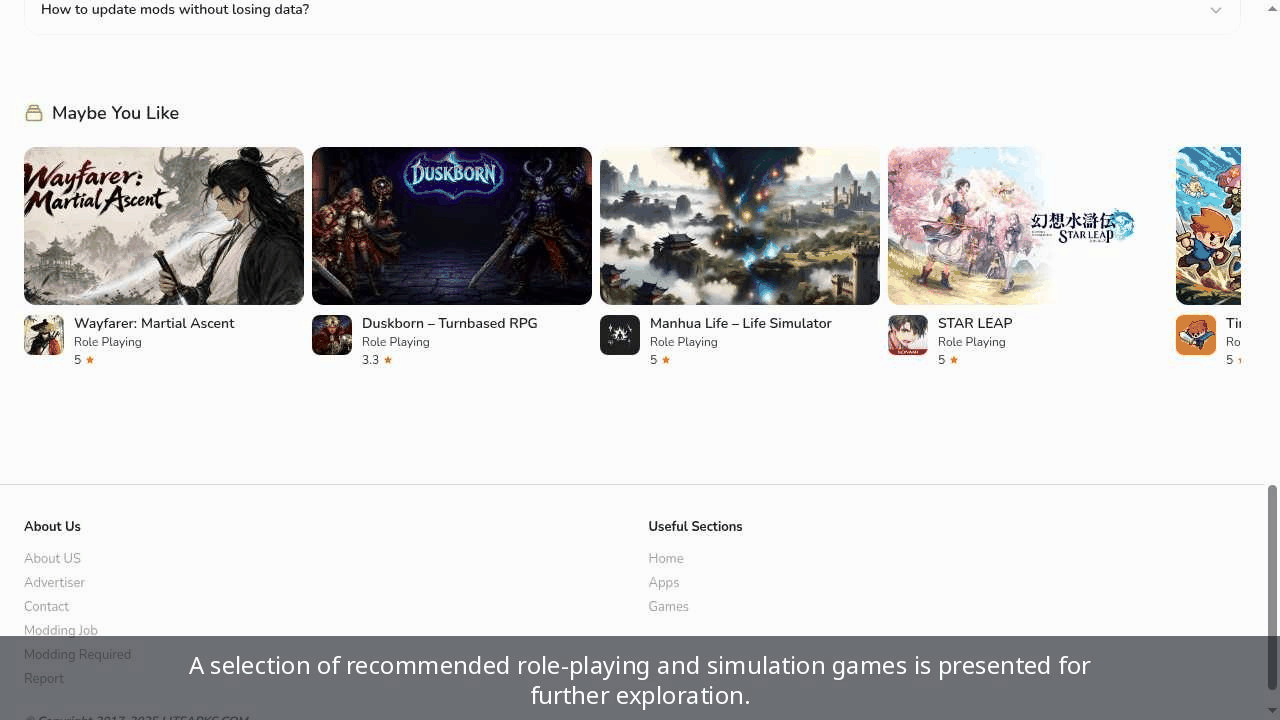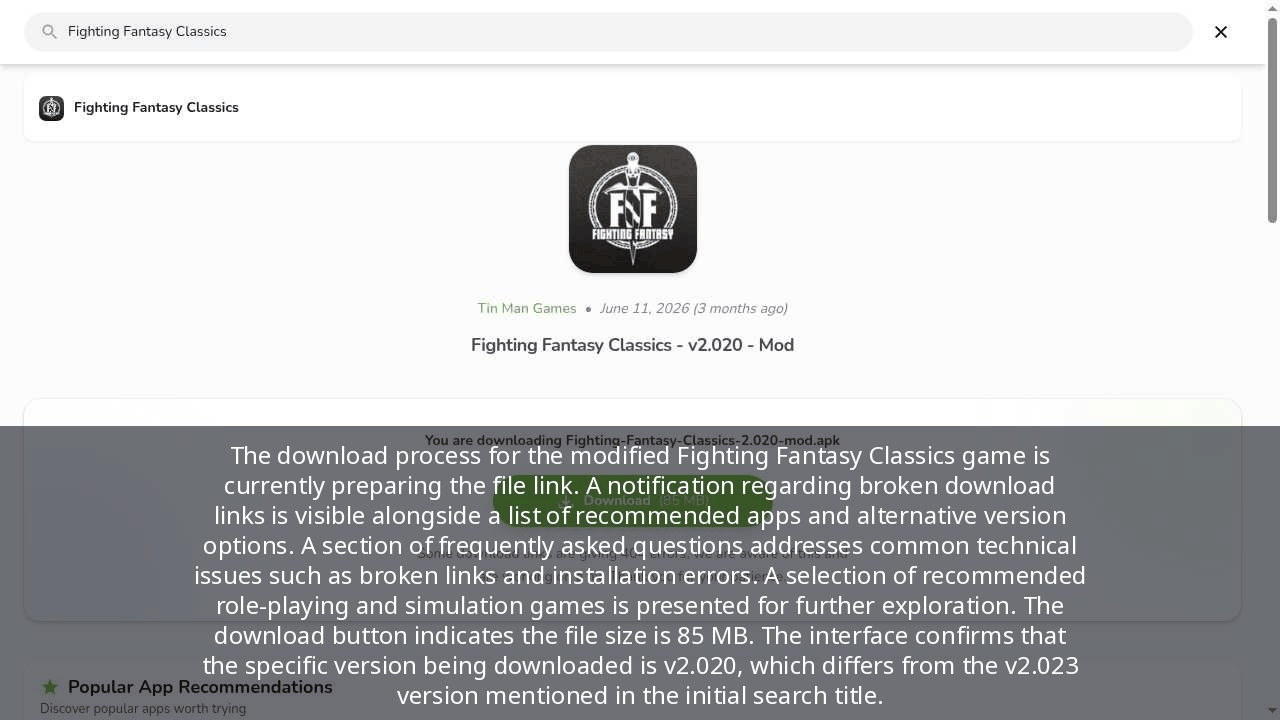
Risk score9/10- The site distributes modded APK files, which are commonly used to bypass licensing and payment protections and frequently contain malware or unwanted code.
- The download process involves a custom APK INSTALLER container that bundles .apk and .obb files, a technique often abused to hide malicious payloads from standard scanners.
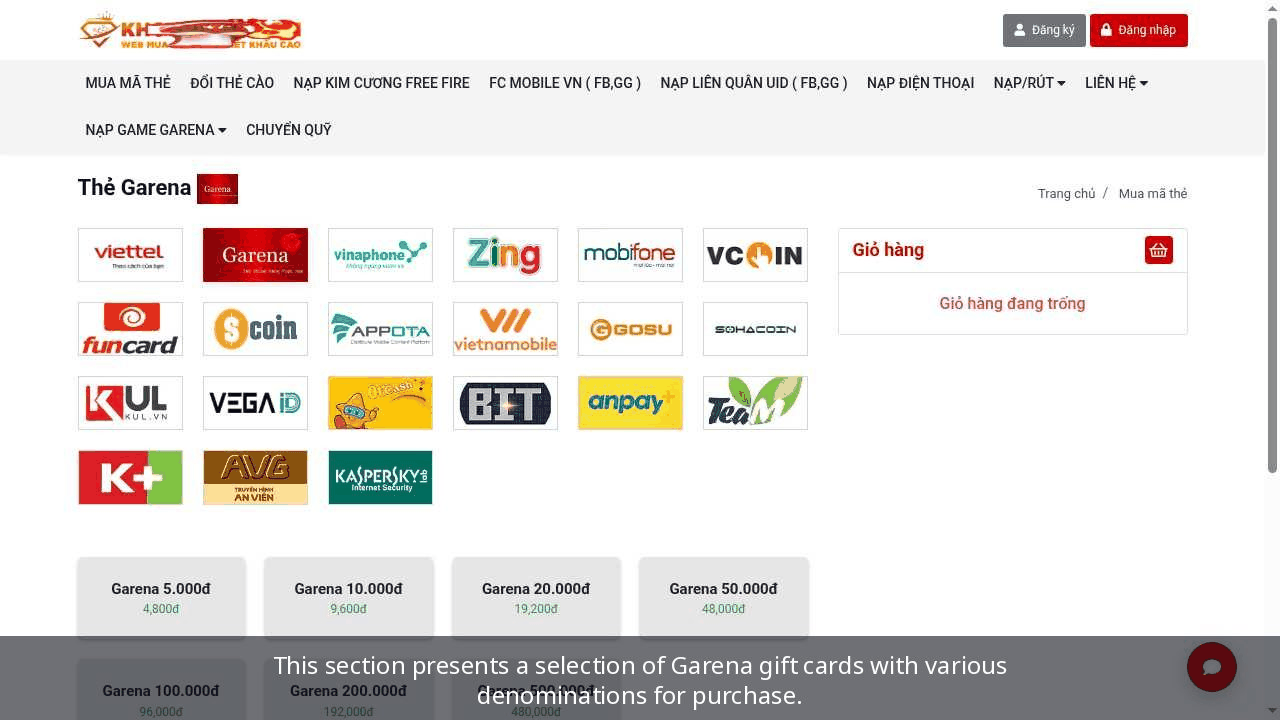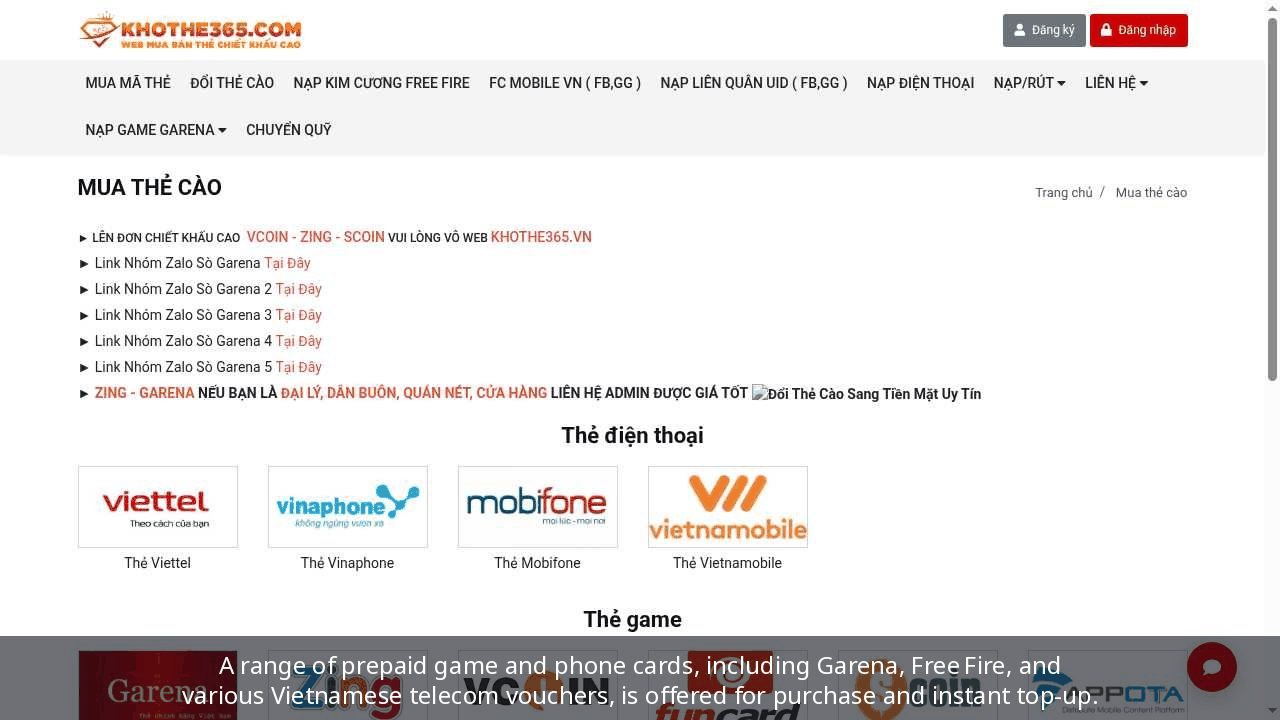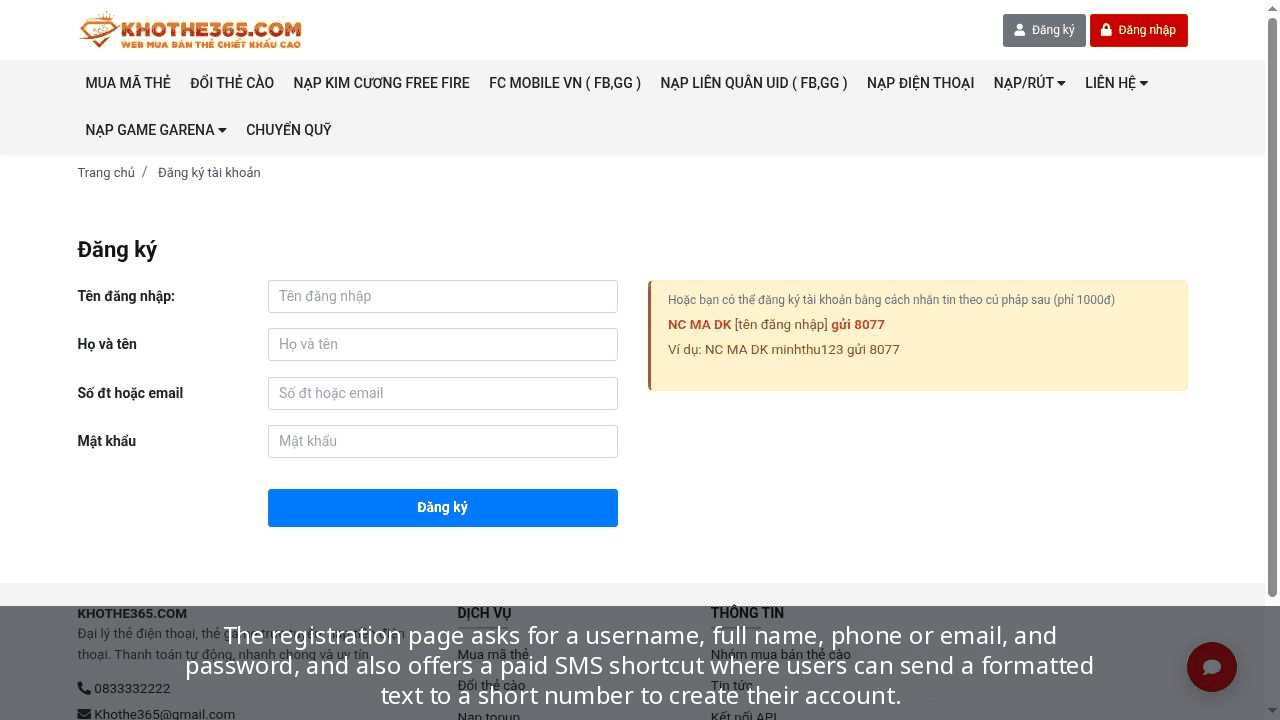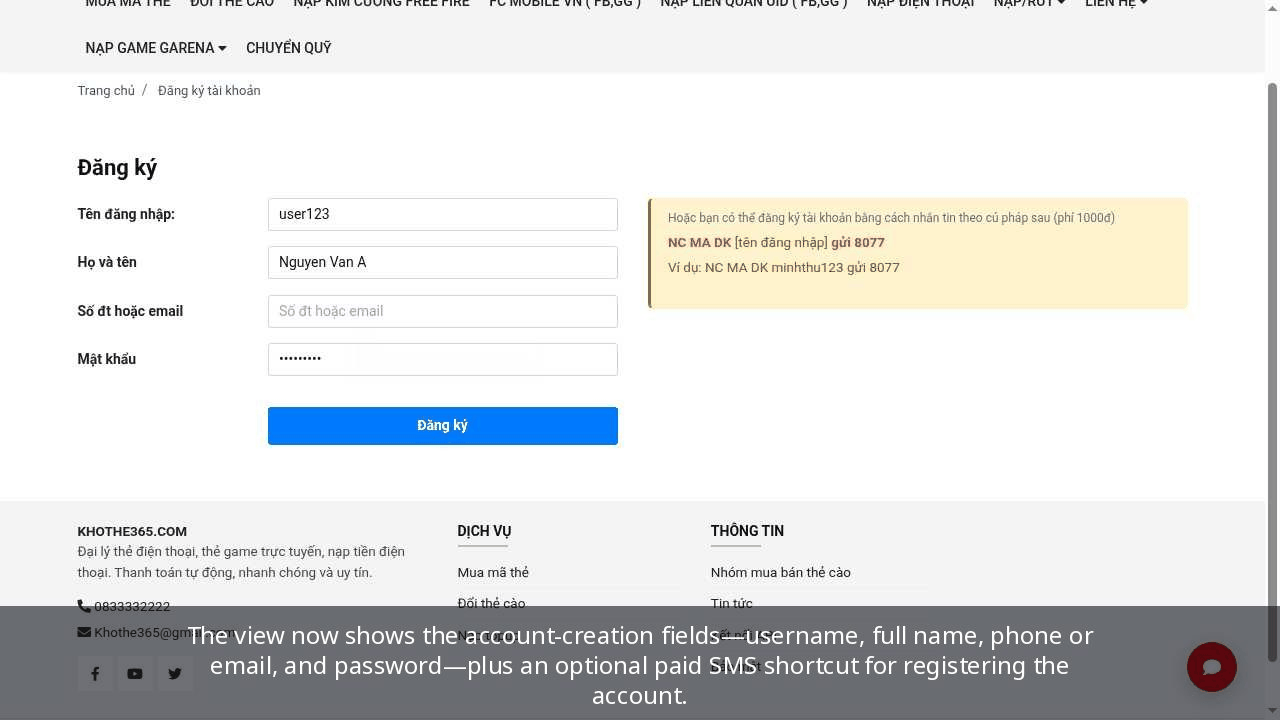
https://khothe365.com/card/the-garena
Risk score9/10- The domain khothe365.com was registered relatively recently in December 2023, which is a common characteristic of fraudulent websites that are quickly created and abandoned.
- The website sells Garena game cards at a consistent 4% discount across all denominations, a pricing pattern frequently associated with scam operations that use stolen payment methods or fraudulent bank accounts to purchase legitimate cards for resale.
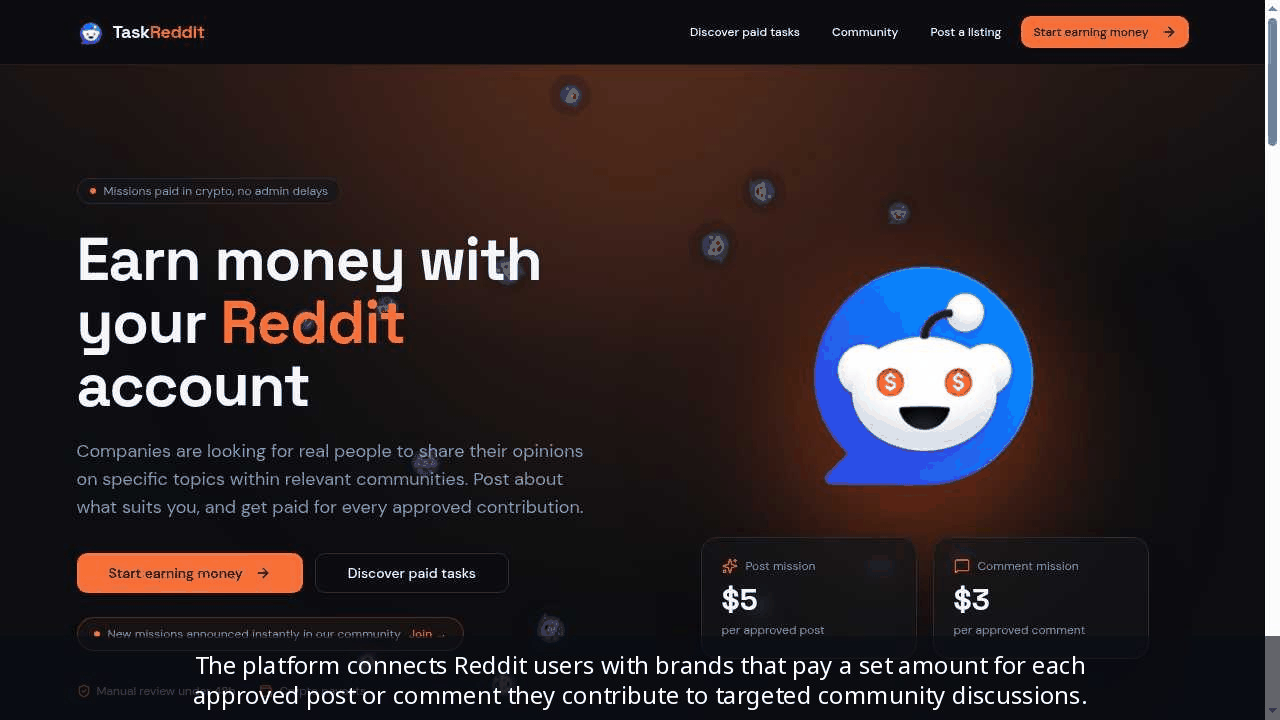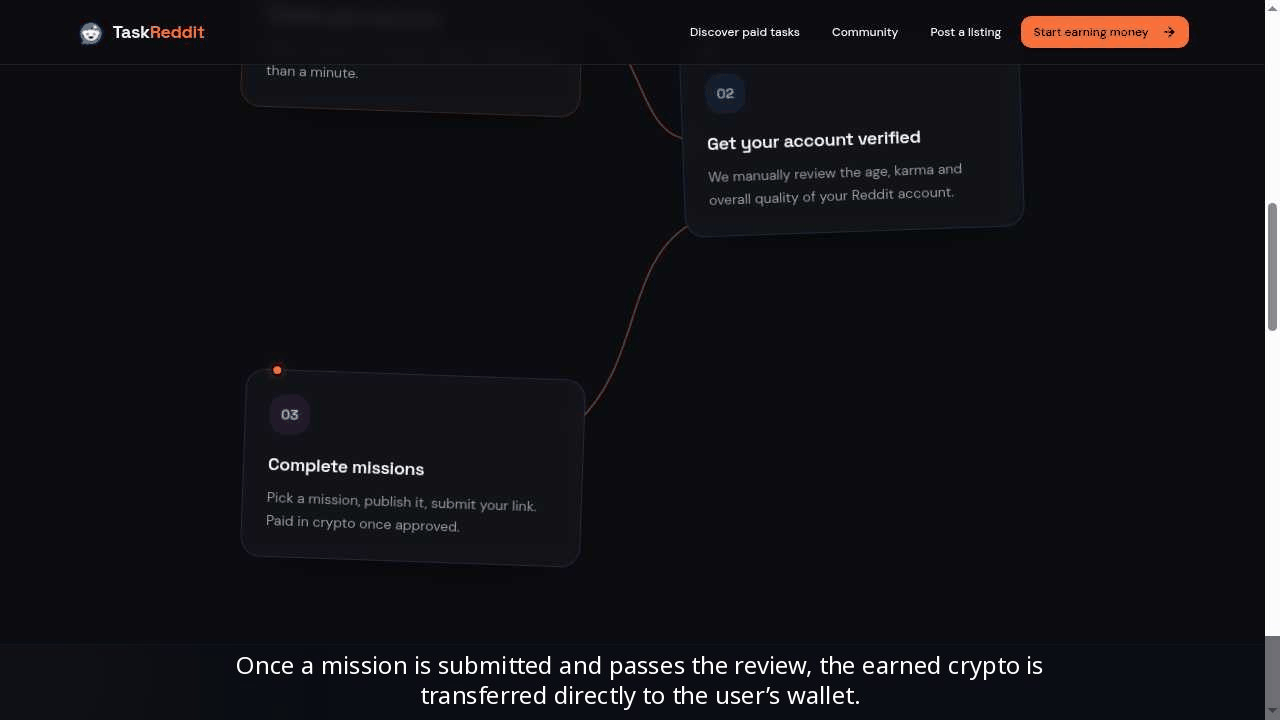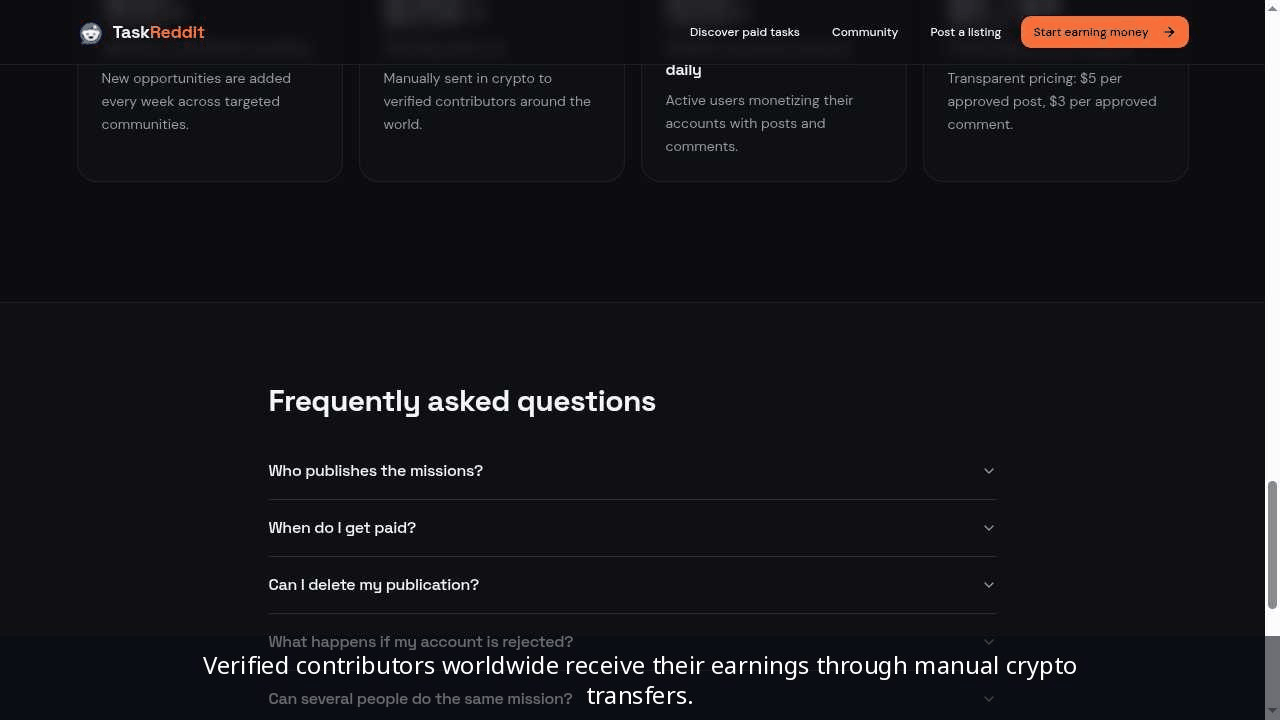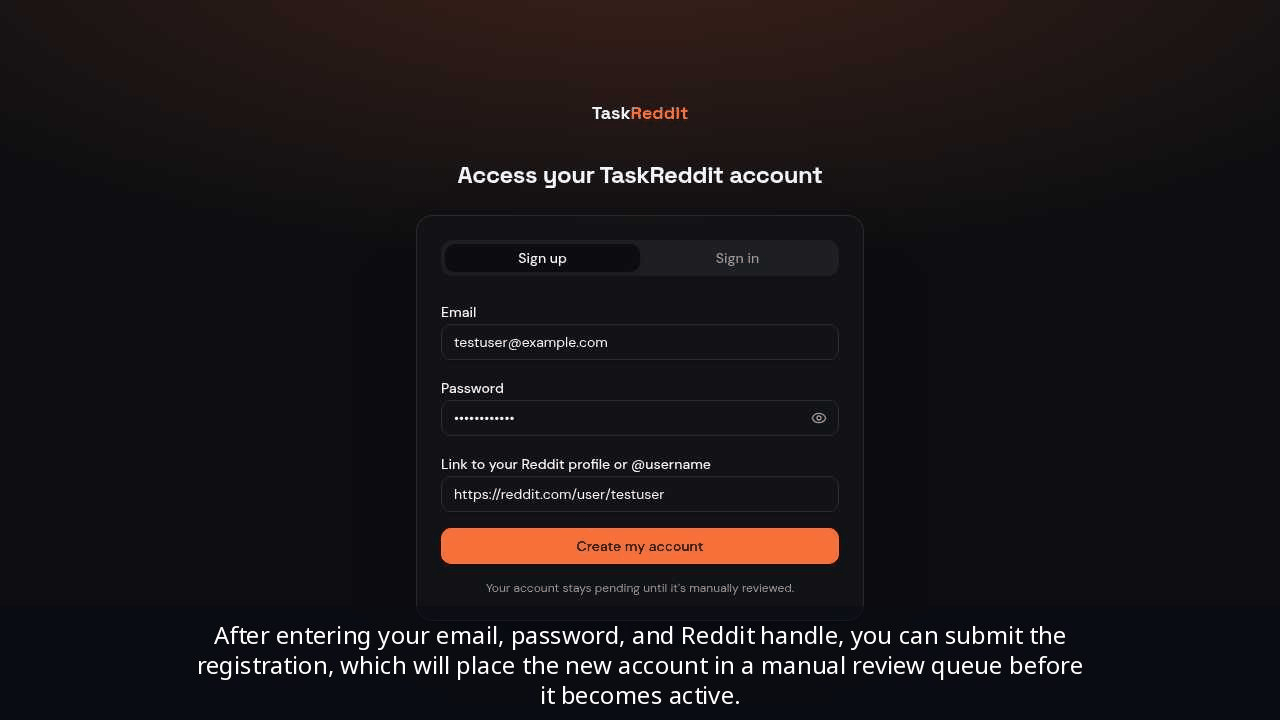
https://reddit-task-money.lovable.app
Risk score9/10- The domain 'reddit-task-money.lovable.app' is a subdomain of 'lovable.app', a free website builder platform, which is commonly abused by threat actors to quickly create and deploy phishing or scam pages without registering dedicated domains.
- The page offers to pay users in cryptocurrency for posting or commenting on Reddit, which is a classic astroturfing and influence-as-a-service scheme used to manipulate public opinion, spread propaganda, or promote scams on social media platforms.
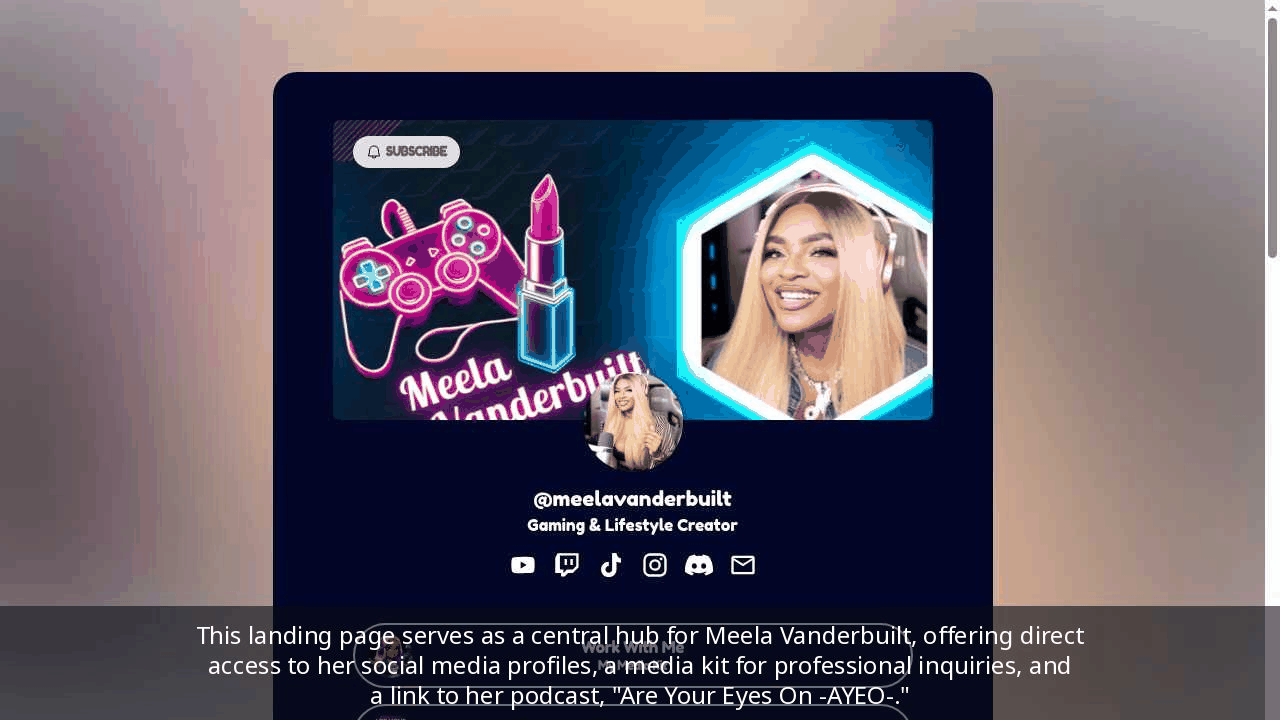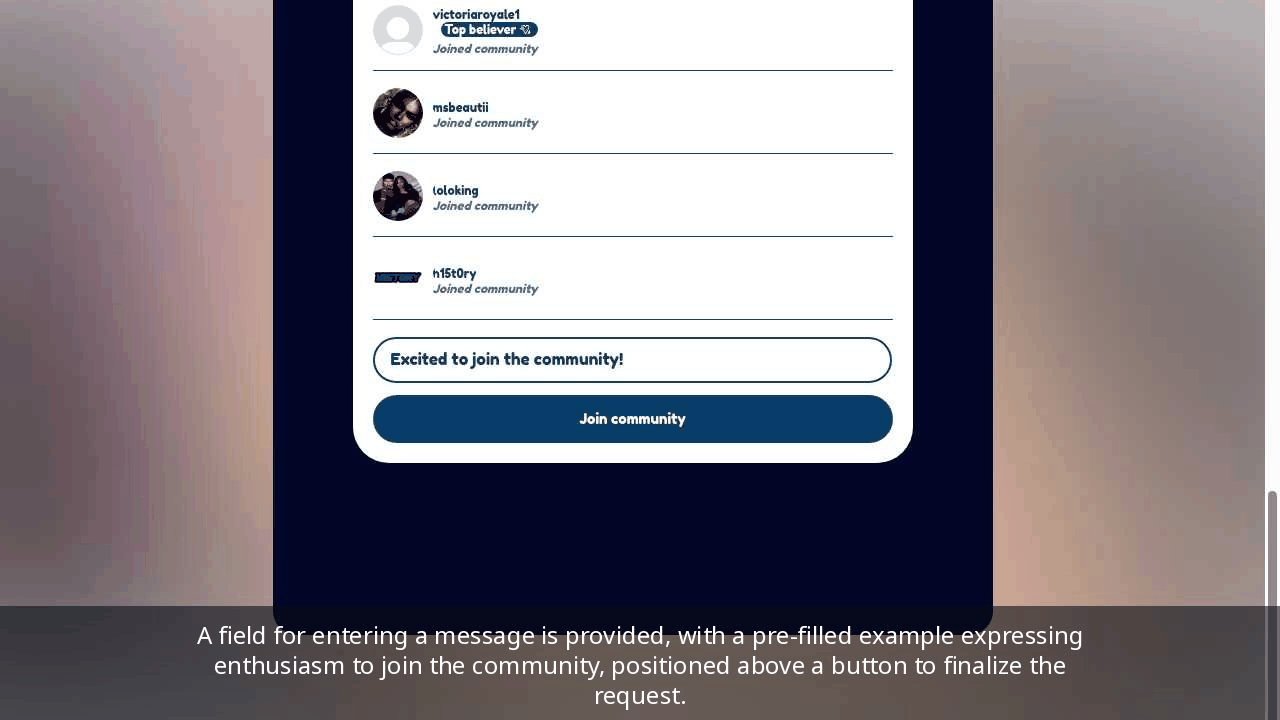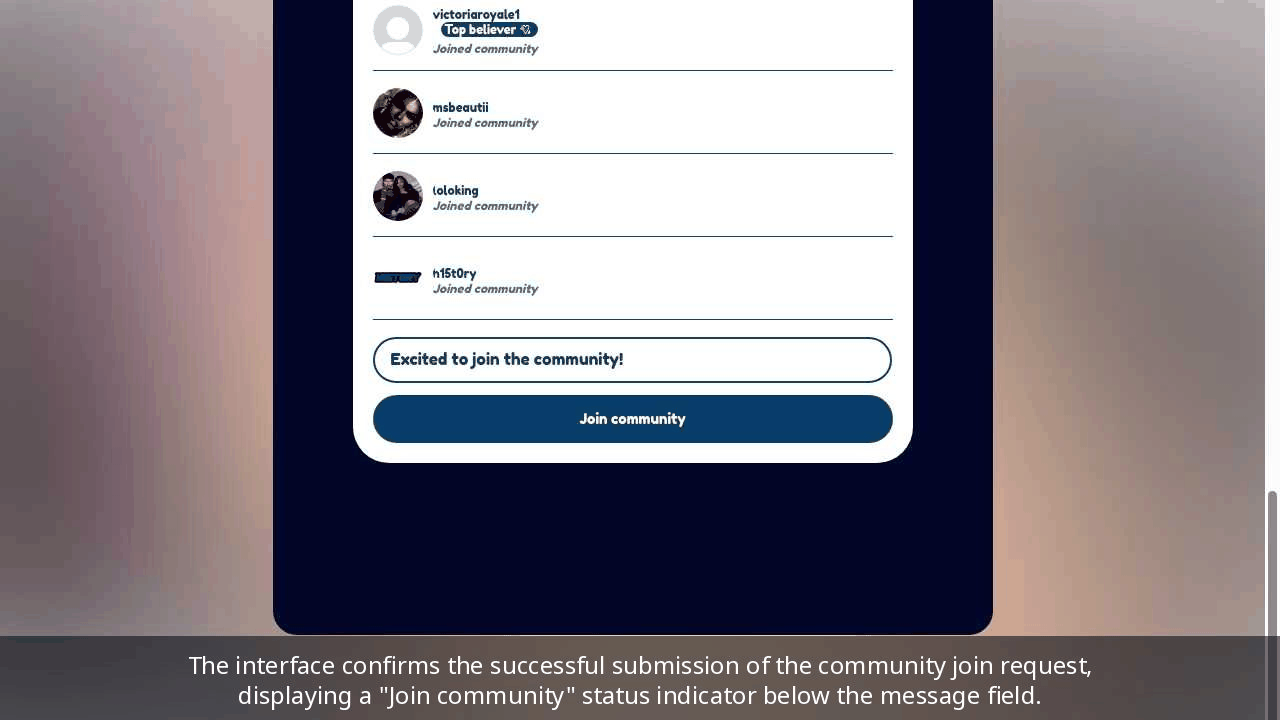
https://meelavanderbuilt.bio
Risk score9/10- The page content consists entirely of an extremely long, repetitive string of Base64-encoded characters with no readable text, images, or functional HTML structure, which is a classic obfuscation technique used to hide malicious payloads or evade content scanners.
- The domain uses a .bio TLD, which is inexpensive and frequently abused for phishing and malware distribution campaigns.
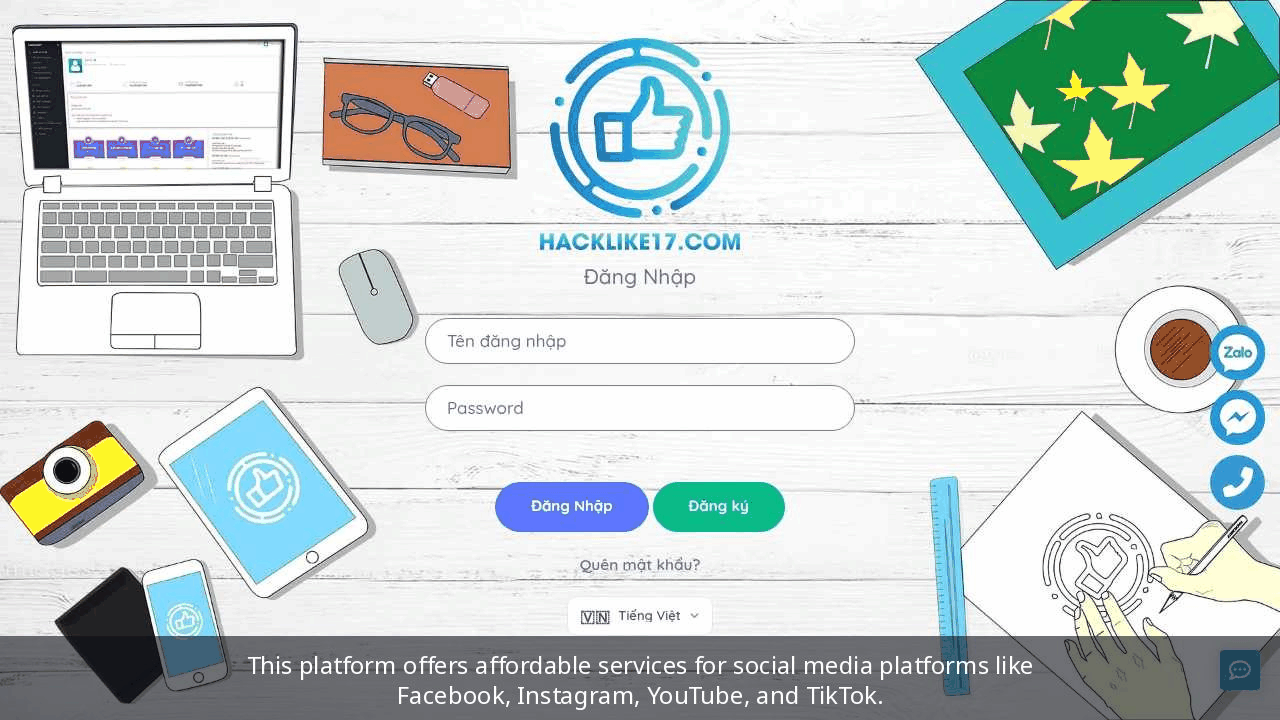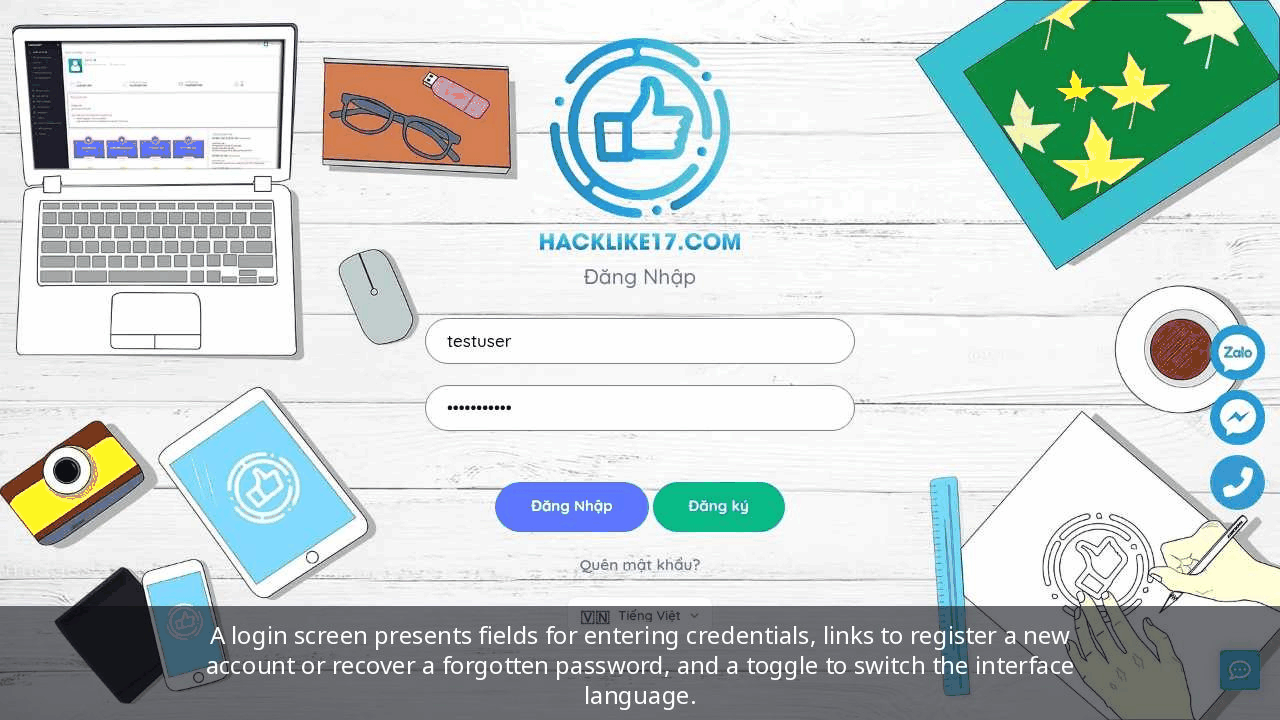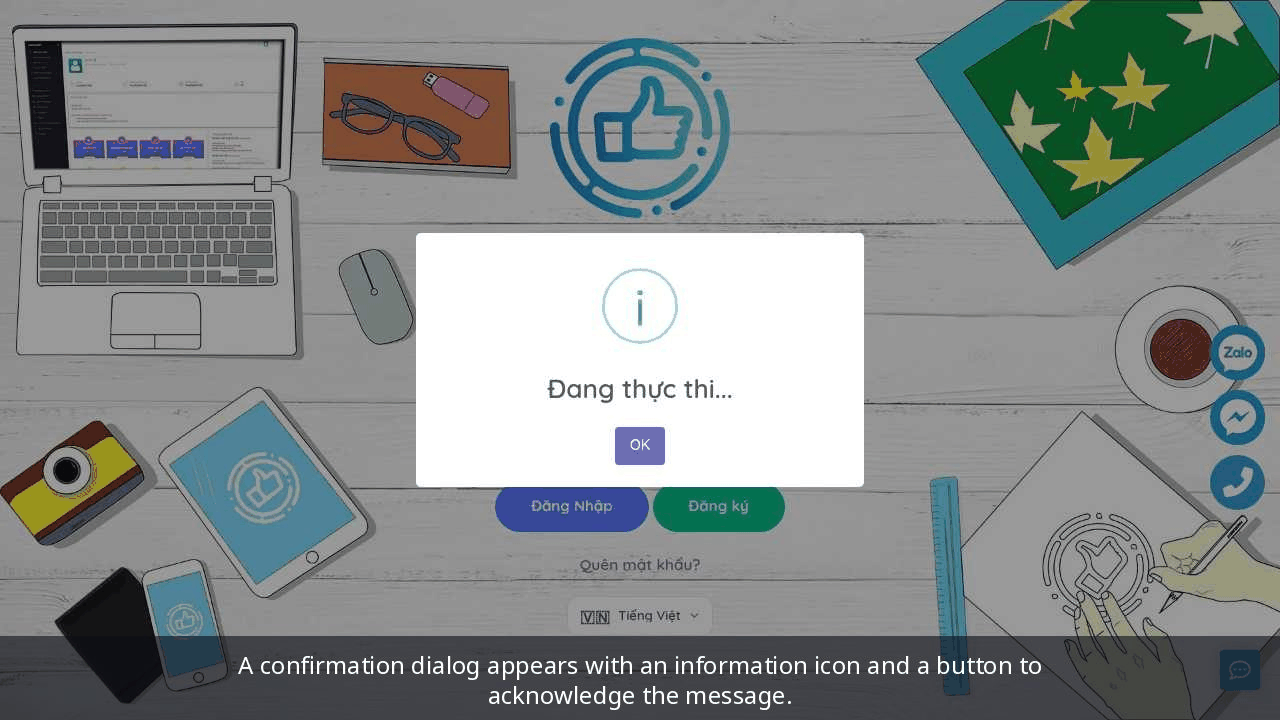
https://hacklike17.com
Risk score9/10- The domain name 'hacklike17.com' contains the word 'hack', which is commonly associated with hacking tutorials, tools, or services, raising immediate suspicion about the site's purpose.
- The page presents a login form requesting a username and password, which is a common vector for credential harvesting phishing attacks.
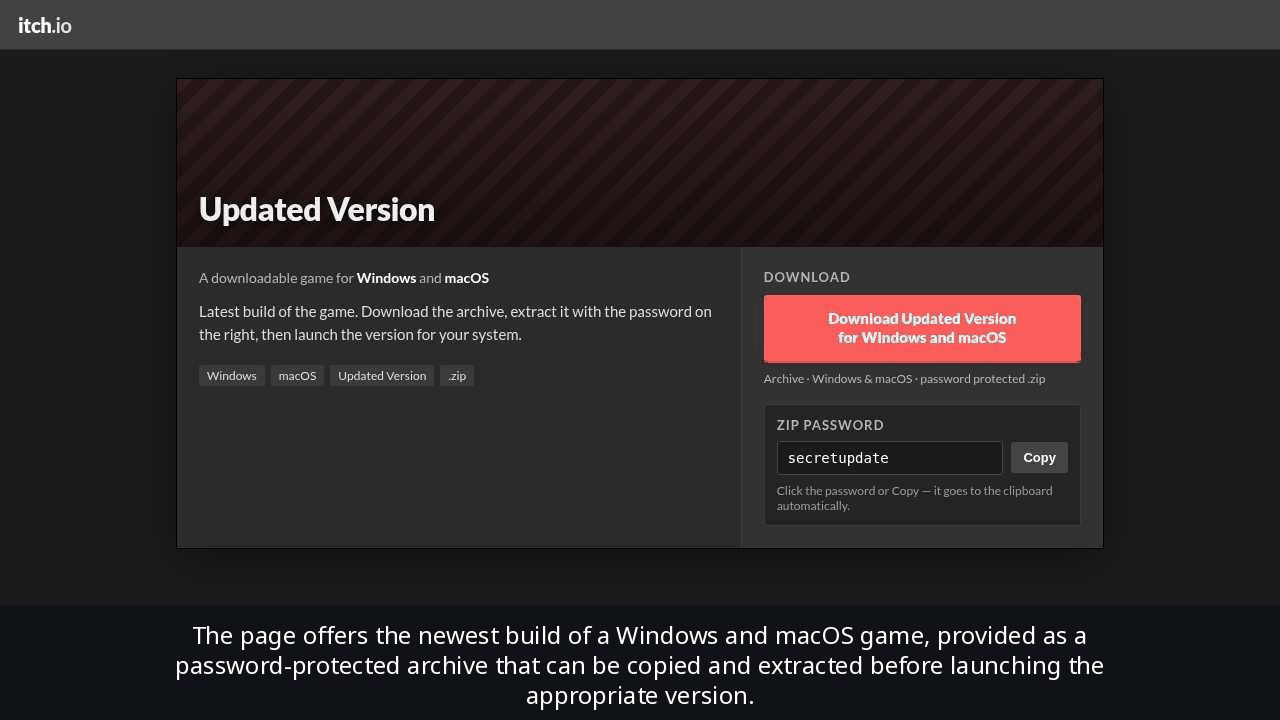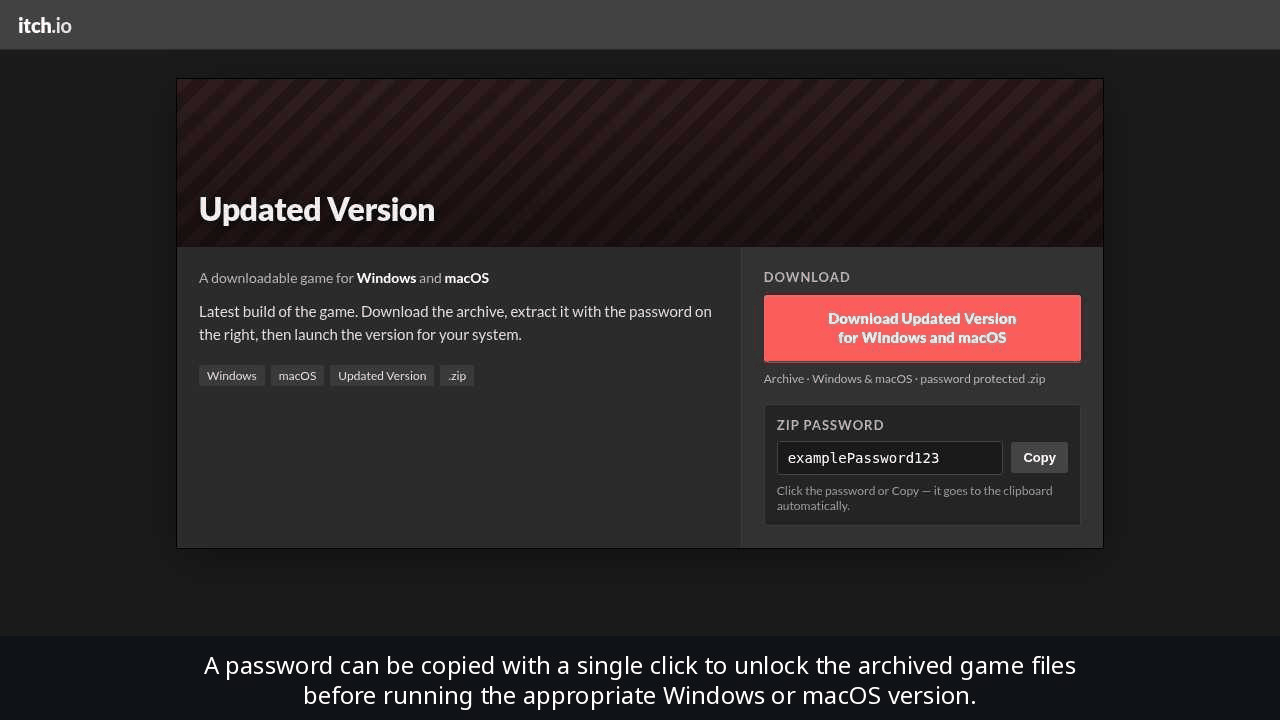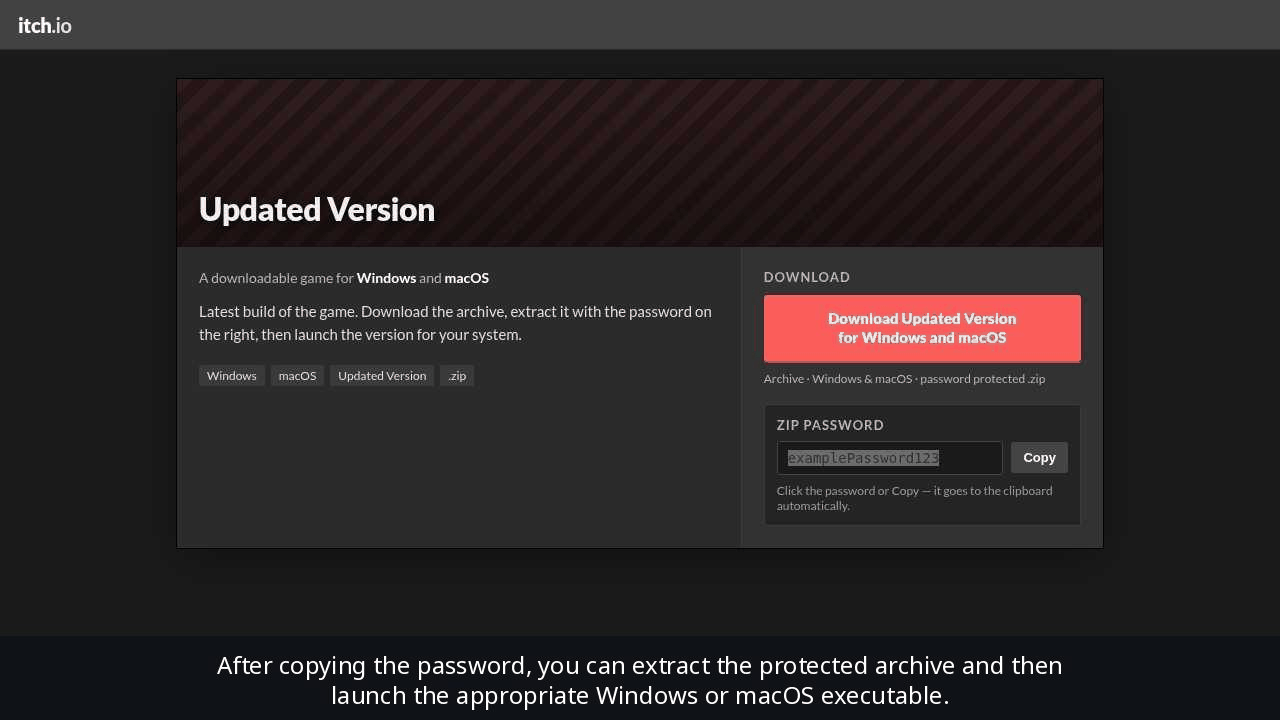
http://aellis-6248.github.io/update
Risk score9/10- The page is hosted on github.io, a legitimate GitHub Pages domain, but the specific path /update on a user repository (aellis-6248) is a common pattern used in phishing and malware distribution campaigns.
- The page mimics an itch.io game download page, presenting itself as an 'Updated Version' downloadable game for Windows and macOS, which is a known social engineering tactic to lure users into downloading malicious archives.
https://aellis-6248.github.io/update
Risk score9/10- The page is hosted on github.io, a legitimate GitHub Pages domain, but the specific path /update under a user repository (aellis-6248) is a common pattern used by threat actors to host malicious payloads.
- The page mimics an itch.io game download page, presenting itself as an 'Updated Version' downloadable game for Windows and macOS, which is a known social engineering tactic to lure users into downloading malware.
https://studio-blender.co.com
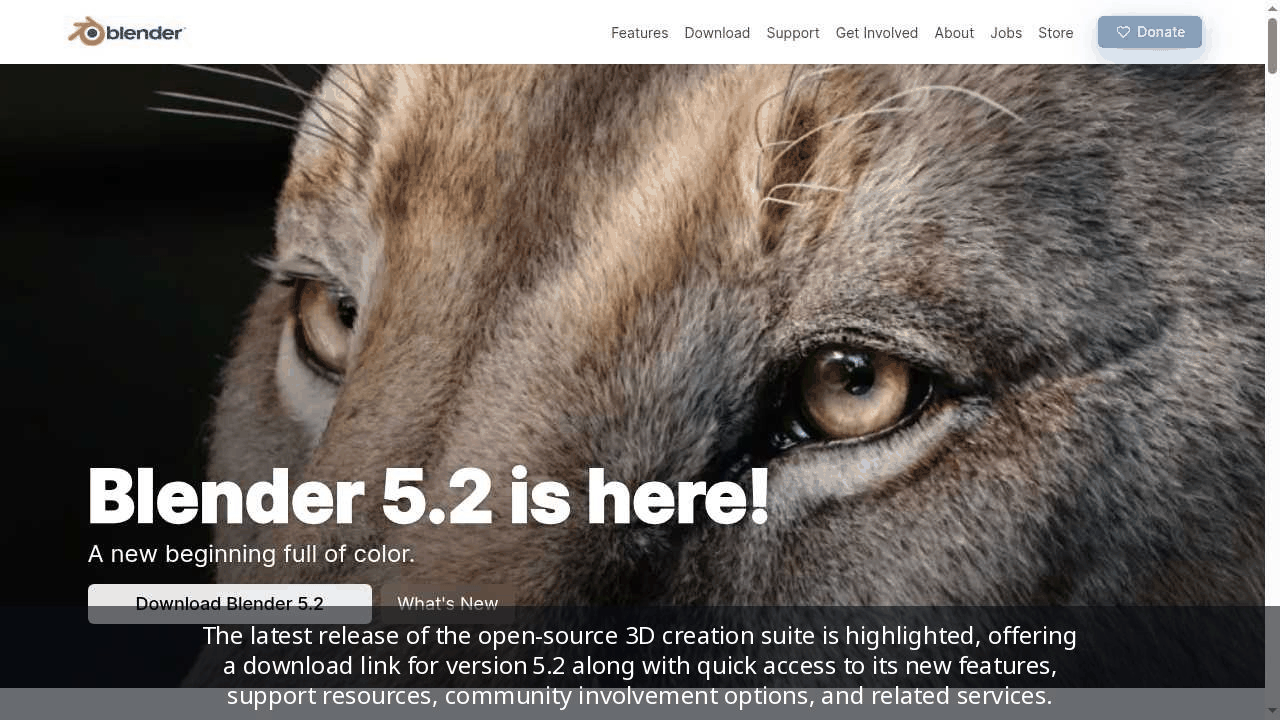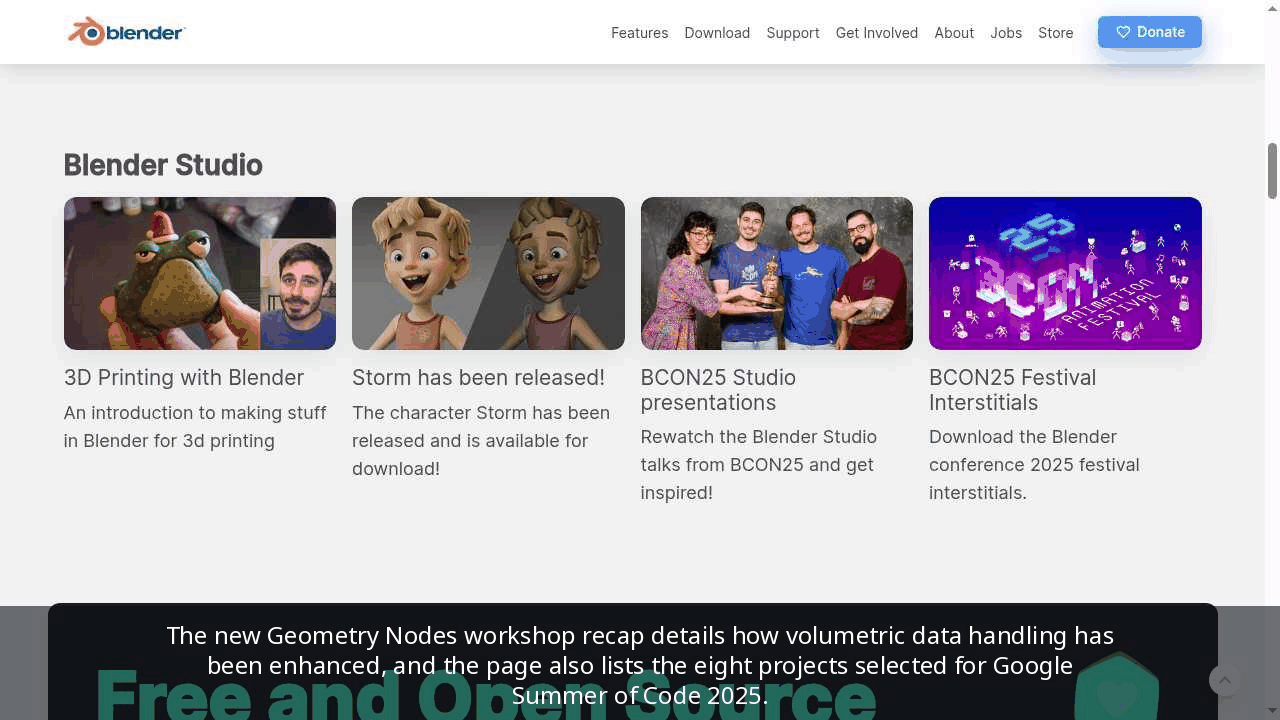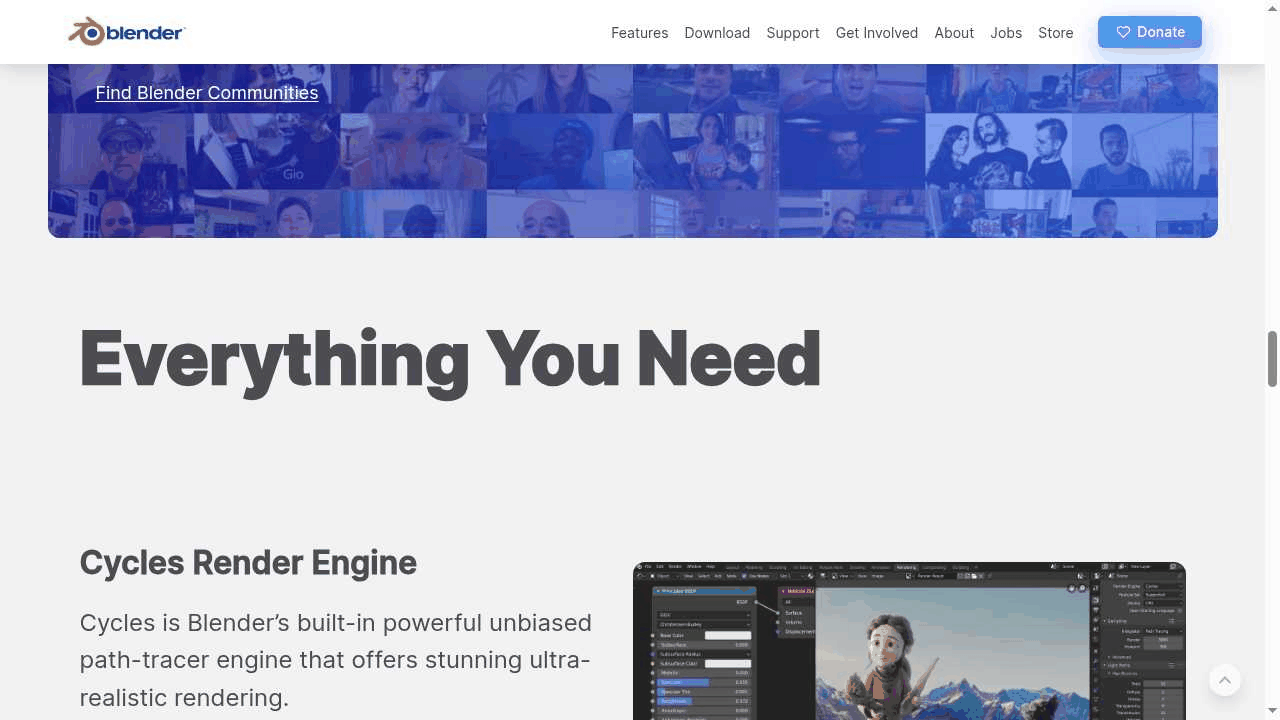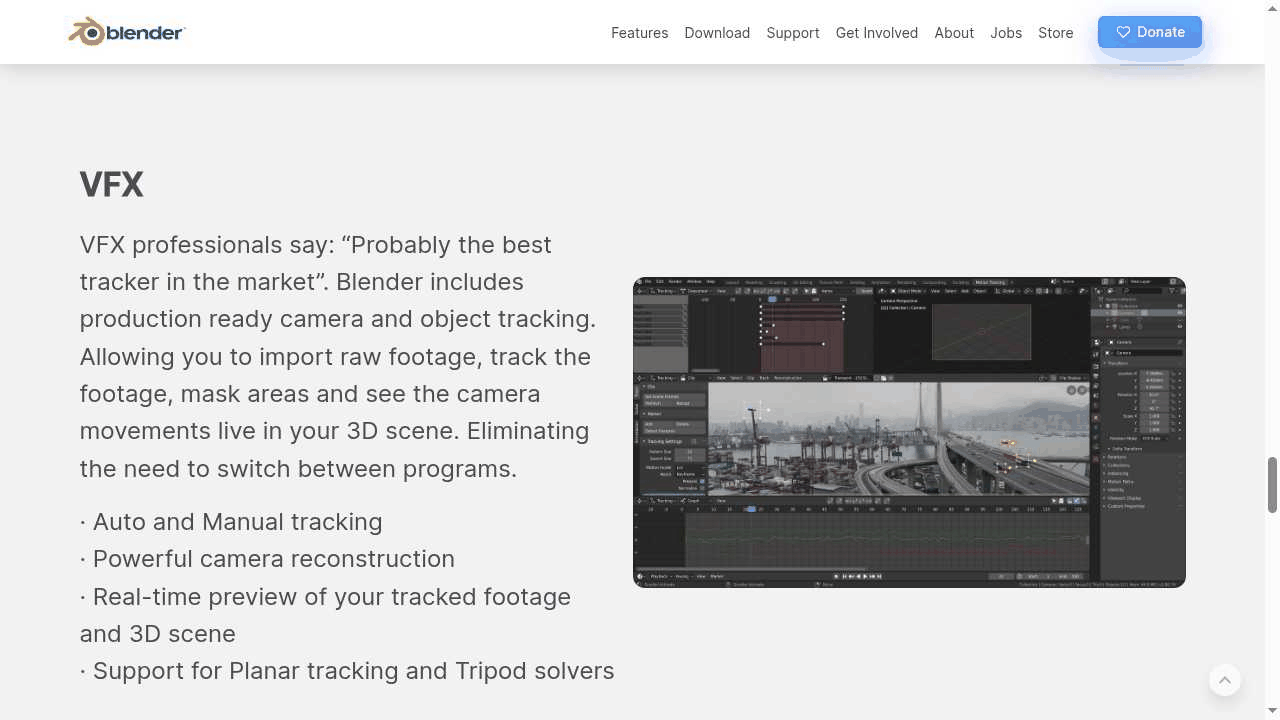
Risk score9/10- The domain studio-blender.co.com is a typosquat of the legitimate blender.org site, using an unusual co.com TLD to mimic the official Blender 3D software project.
- The page content is a near-exact copy of the official Blender website, including branding, navigation, and feature descriptions, indicating it was cloned to deceive visitors.
Miễn trừ trách nhiệm: Chúng tôi không đảm bảo kết quả chính xác và không chịu trách nhiệm cho bất cứ điều gì.