Malicious websites today
14,348
Malicious websites this week
116,645
Malicious websites this month
766,833
Total malicious websites
21,722,000
TLD distribution
- .com - 50.2%
- .top - 17.1%
- .xyz - 10.1%
- .cc - 6.3%
- .buzz - 3.4%
- .shop - 3.3%
- .net - 3.0%
- .cn - 2.6%
- .org - 2.3%
- .info - 1.8%
Threat trend
21.1M21.3M21.5M21.7M
Threats14/0920/0926/0901/1007/1013/10
Recent threats
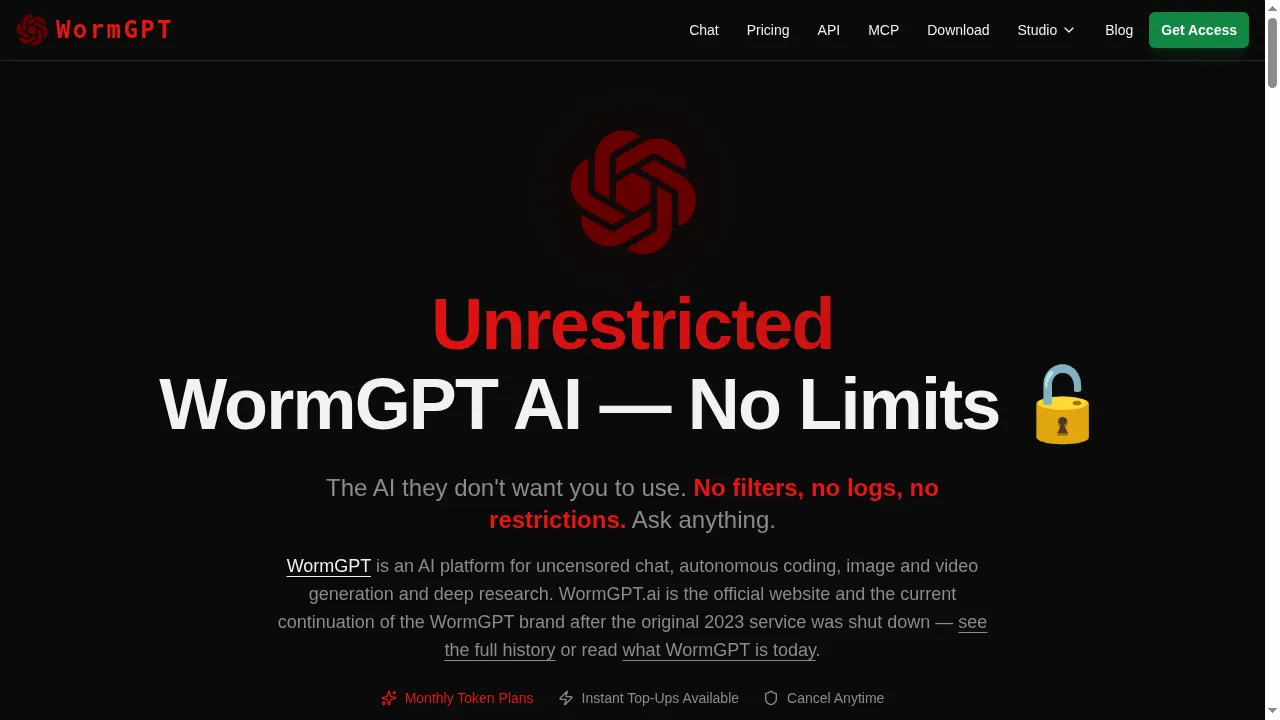
https://wormgpt.ai
Risk score9/10- The site promotes WormGPT, a brand tied to the 2023 malicious AI tool built for cybercrime, and offers an 'unrestricted' AI with no filters, no refusals and no logs, which is a typical marketing pitch for criminal-use LLM services.
- It advertises an autonomous AI Security Agent that automates reconnaissance, vulnerability scanning and exploit research, plus dark web and .onion discovery and threat actor profiling, all with no content restrictions. This supports offensive misuse such as malware, phishing and intrusion.
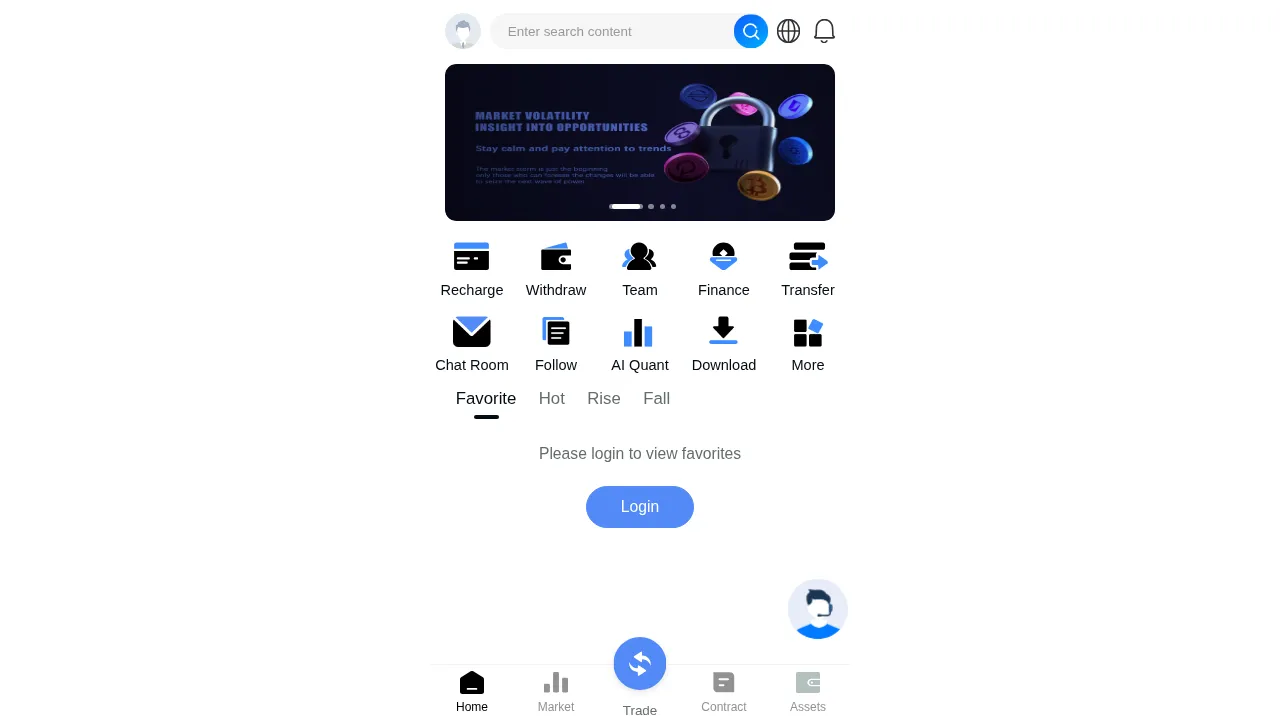
https://usdc661.com
Risk score9/10- The domain usdc661.com was registered on November 9, 2025, under a privacy-style registrant (KH), so it is a very young domain with no established reputation, which is typical of throwaway scam infrastructure.
- The page is a generic mobile-style crypto trading platform with Recharge, Withdraw, Team, Finance, AI Quant, Follow, Contract and Chat Room features, a template commonly used in fraudulent crypto investment and pig-butchering scams.
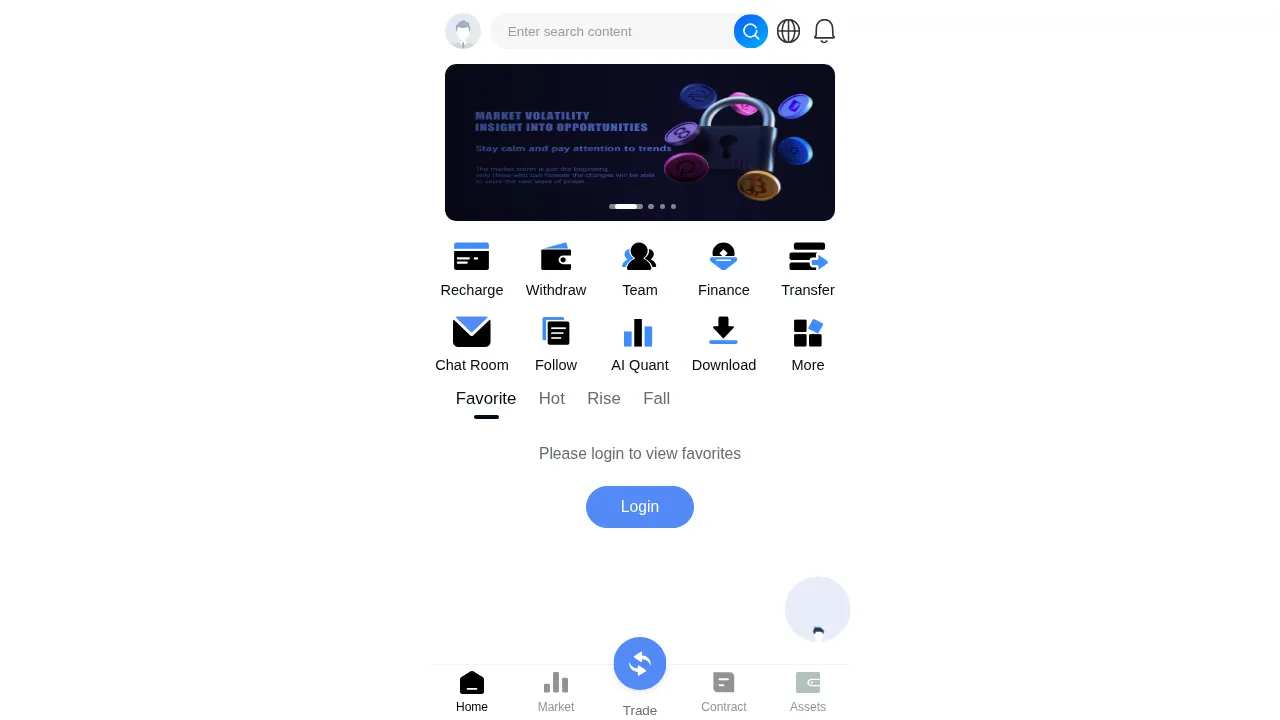
https://usdc336.com
Risk score9/10- The site presents itself as a cryptocurrency trading platform with Recharge, Withdraw, Team, Finance, Transfer, Chat Room, Follow, and AI Quant features. This combination is typical of fraudulent investment and pig-butchering scam platforms.
- The domain usdc336.com was registered recently, on November 9, 2025, with a registrant listed only as KH. It uses a generic stablecoin-style name with random digits, which is common for disposable scam domains.
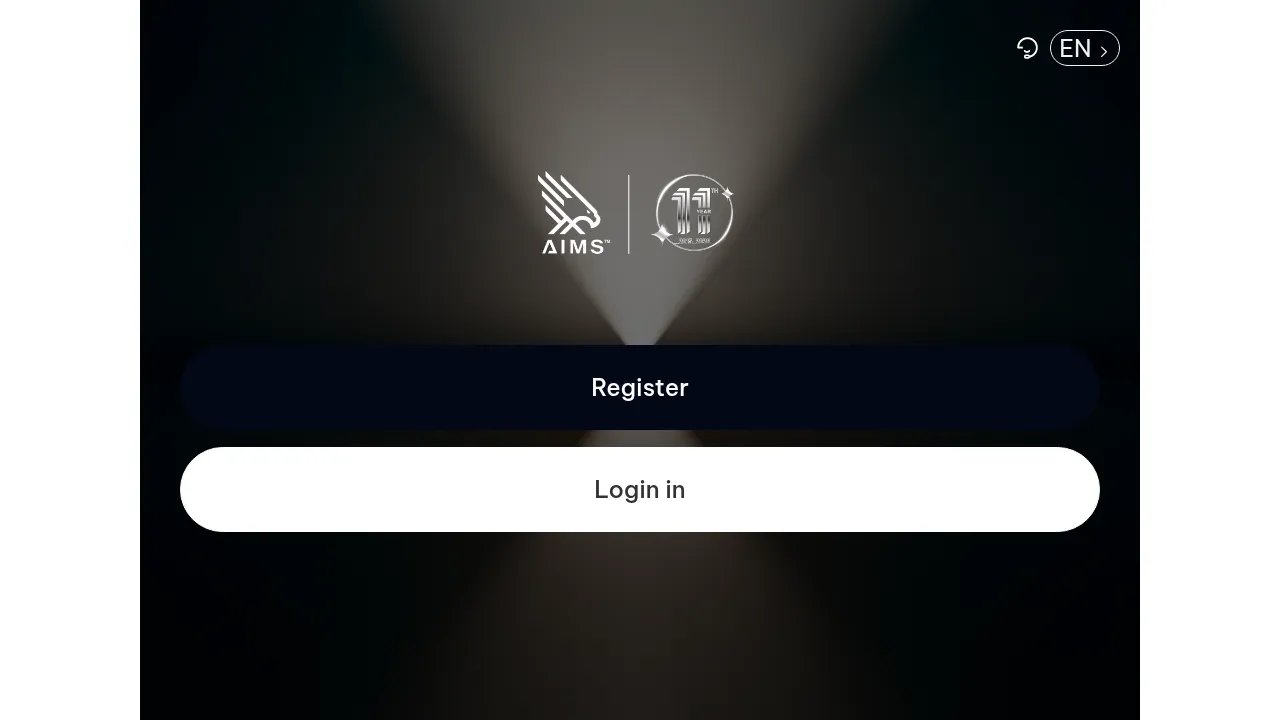
https://app.aimsglobalvn.com/login
Risk score9/10- The page is a trading platform login portal that imitates AIMS, a forex and CFD broker brand, using its logo and an '11 year' anniversary badge to look established and legitimate.
- The domain aimsglobalvn.com was registered only about five weeks before the analysis date. A brand's real platform would normally sit on a long-established domain, so this is a strong sign of a throwaway fraudulent site.
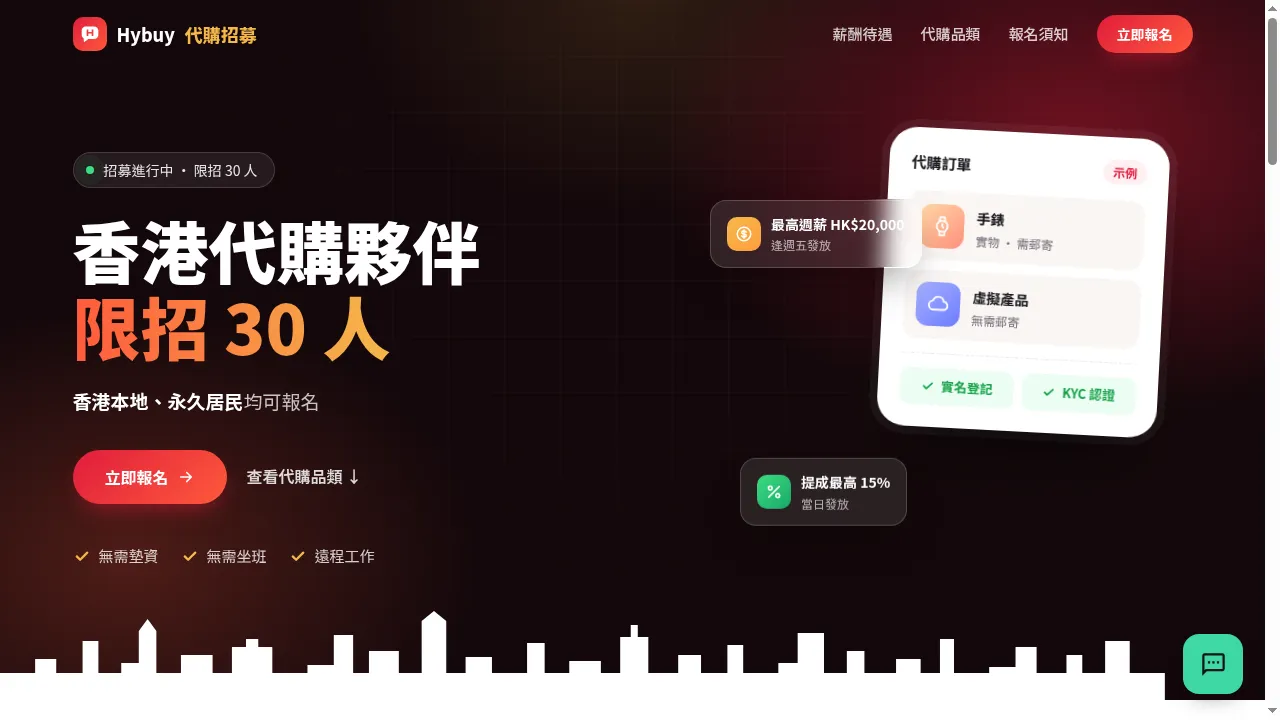
https://hybuyers.world
Risk score9/10- The page advertises a remote 'purchasing agent' job in Hong Kong with unrealistic pay of up to HK$20,000 per week plus up to 15% commission paid the same day, a classic recruitment scam lure.
- The domain hybuyers.world was registered only one day ago and uses an unusual .world TLD, while the page claims the company was founded in 2015 and serves 2 million customers, which is inconsistent and suggests brand impersonation.
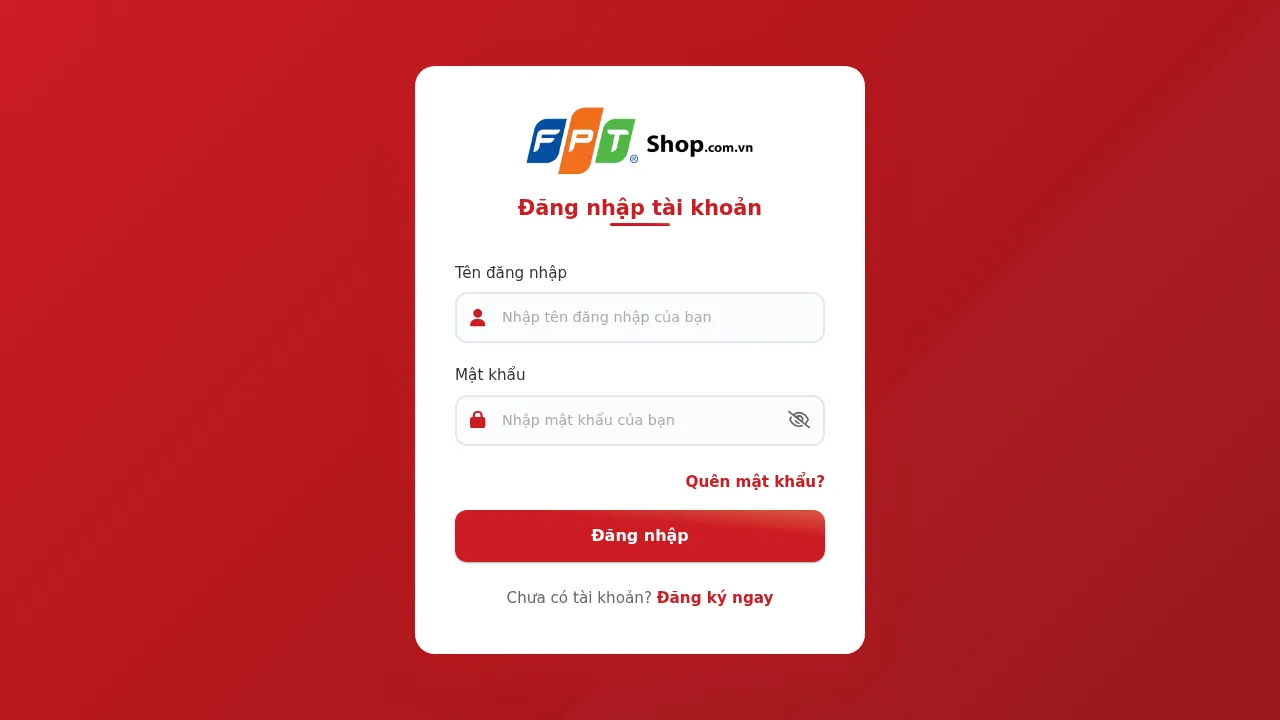
https://fptshopsalevns.com
Risk score9/10- The domain fptshopsalevns.com was registered very recently on August 15, 2026, which is only about two months before the current date, indicating a newly created domain often associated with phishing campaigns.
- The domain name fptshopsalevns.com is a deceptive variation of the legitimate FPT Shop domain (fptshop.com.vn), designed to impersonate the well-known Vietnamese electronics retailer to trick users.
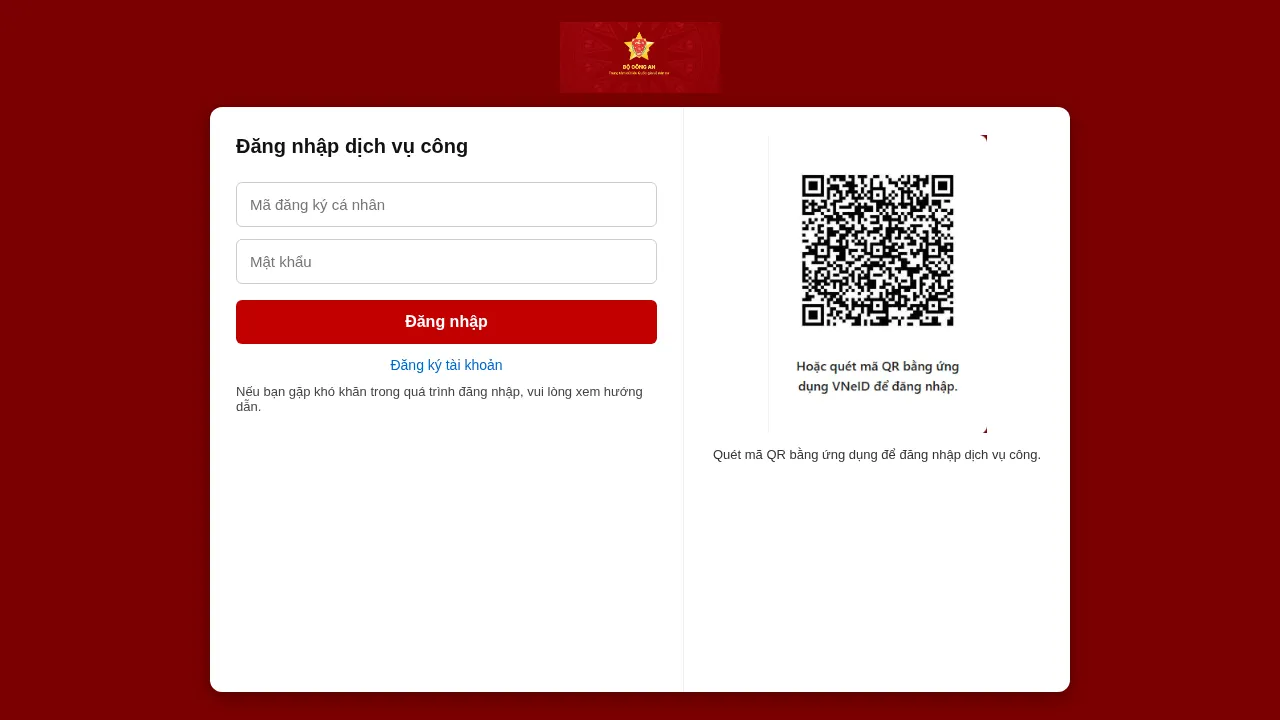
https://dichvucongkekhai.com
Risk score9/10- The domain was registered very recently on November 18, 2025, which is a common indicator of throwaway phishing infrastructure.
- The domain name 'dichvucongkekhai' mimics the legitimate Vietnamese government public service portal 'dichvucong.gov.vn', suggesting a deliberate impersonation attempt.
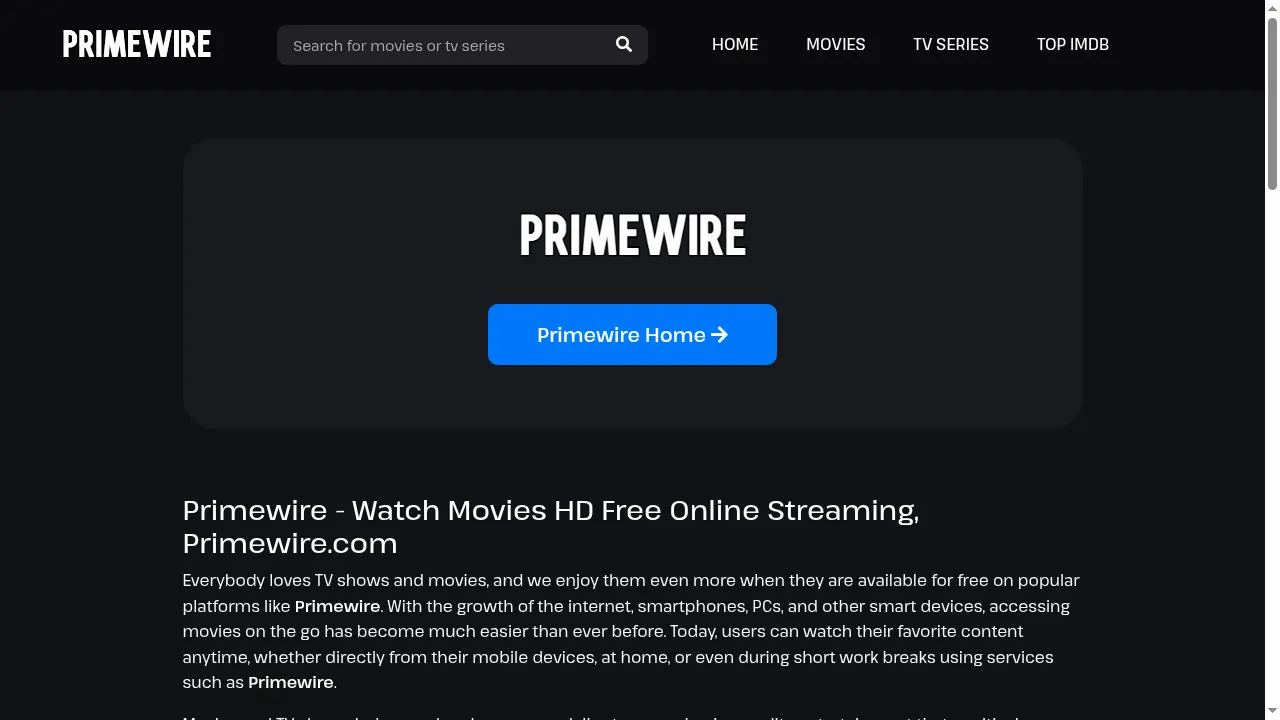
https://primewire.buzz
Risk score9/10- The domain primewire.buzz was registered very recently, on July 16, 2026, which is only a few months old and consistent with the pattern of piracy sites that frequently reappear under new domain extensions after being shut down.
- The site explicitly describes itself as a piracy platform, stating it does not host content but links to third-party sources hosting copyrighted material, and openly acknowledges being labeled as a piracy website and distributor of copyrighted material.
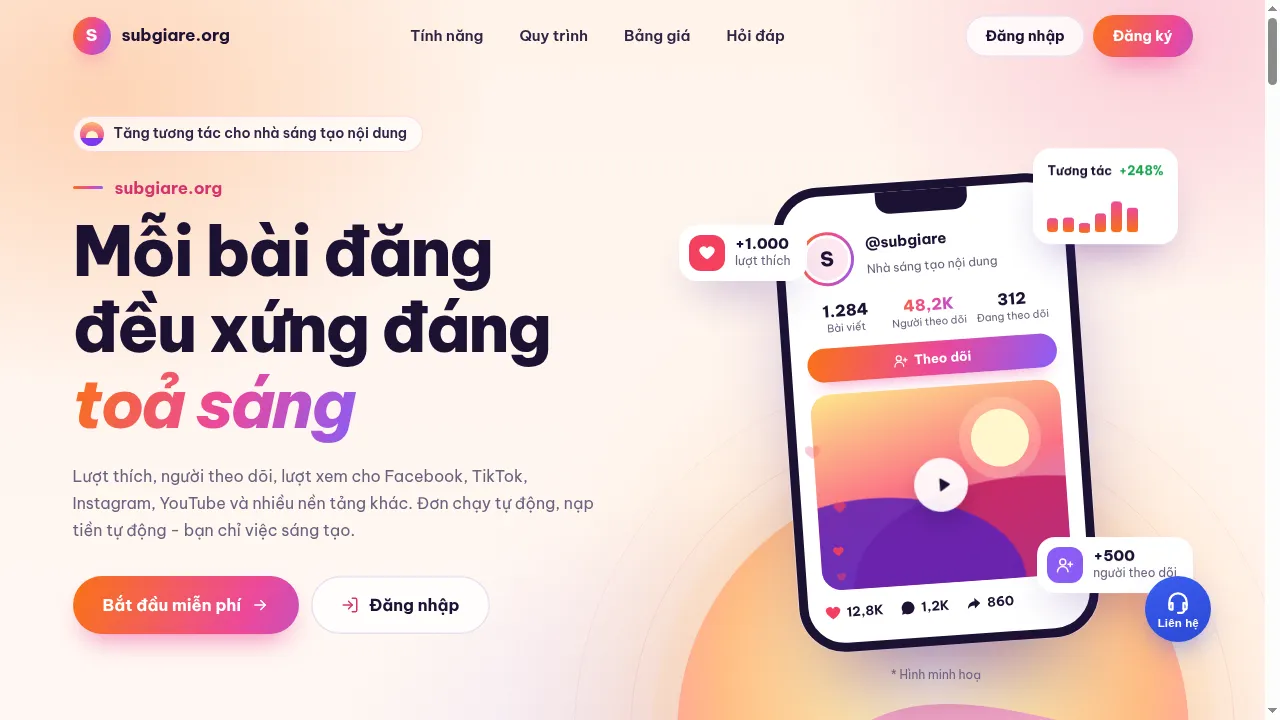
https://subgiare.org
Risk score9/10- The website subgiare.org is a Vietnamese-language service that sells artificial engagement metrics including likes, followers, views, and live stream viewers for major social media platforms such as Facebook, TikTok, Instagram, YouTube, Twitter/X, Threads, Shopee, Lazada, and Telegram.
- The service explicitly advertises the ability to boost followers, likes, and views, which violates the terms of service of every social media platform it targets and constitutes a form of engagement manipulation or fake engagement fraud.
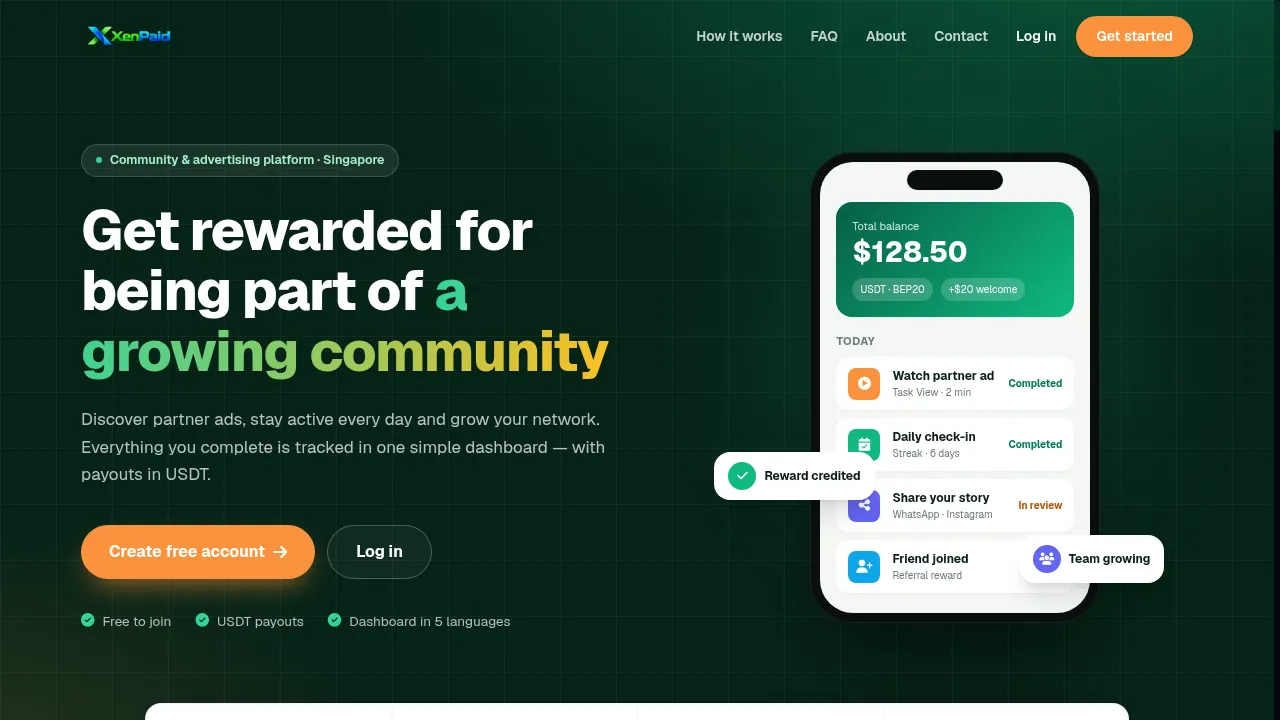
https://xenpaid.com
Risk score9/10- The site presents itself as a community and advertising platform that pays users in USDT (BEP20) for completing simple tasks such as watching partner ads, daily check-ins, sharing stories on social media, and recruiting referrals, which is a classic structure for a paid-to-click or task-based reward scam.
- The platform heavily emphasizes referral and recruitment mechanics, including level rewards for building a team and a $20 welcome bonus, which are hallmark indicators of a pyramid or Ponzi-style scheme that relies on continuously recruiting new members to sustain payouts.
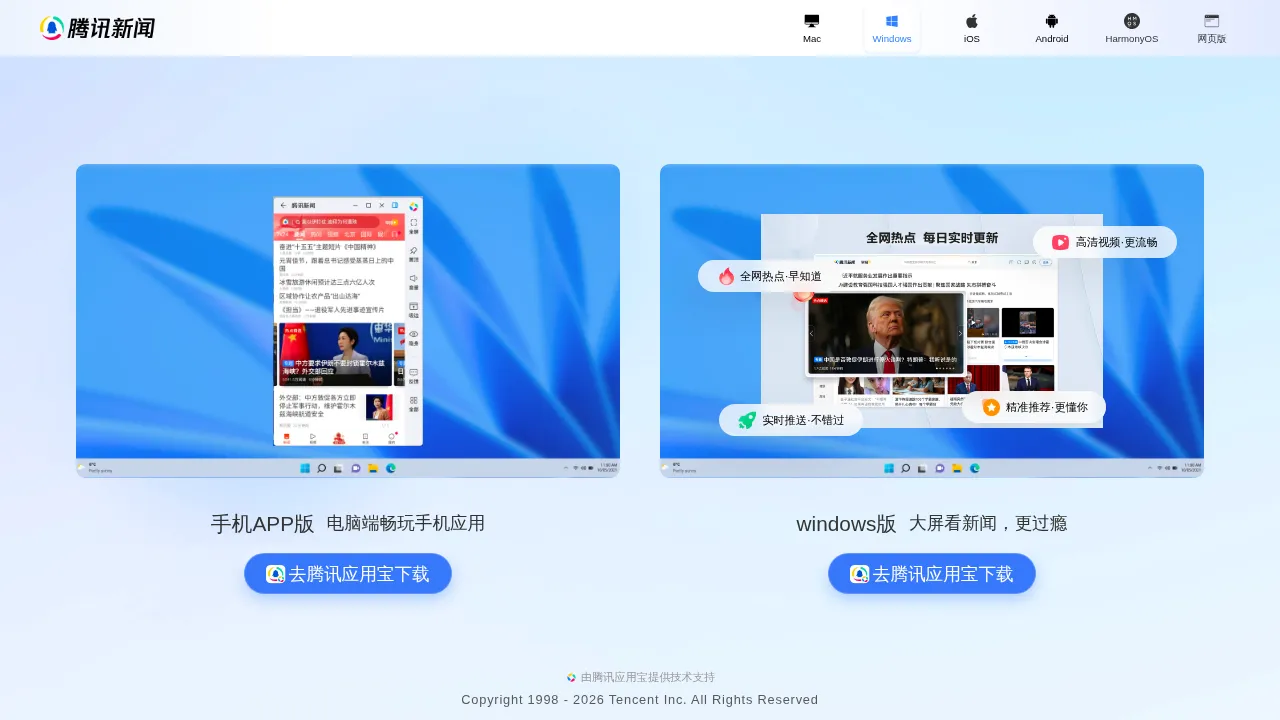
https://73nug9s.scsewlm.cn/80177d45-874e-41ae...
Risk score9/10- The initial URL points to a suspicious subdomain on scsewlm.cn, which is a recently registered domain with a Chinese individual registrant, suggesting it was set up specifically for this campaign.
- The URL path contains a UUID-style identifier, a common technique used in malicious redirect chains to track individual victims or sessions.
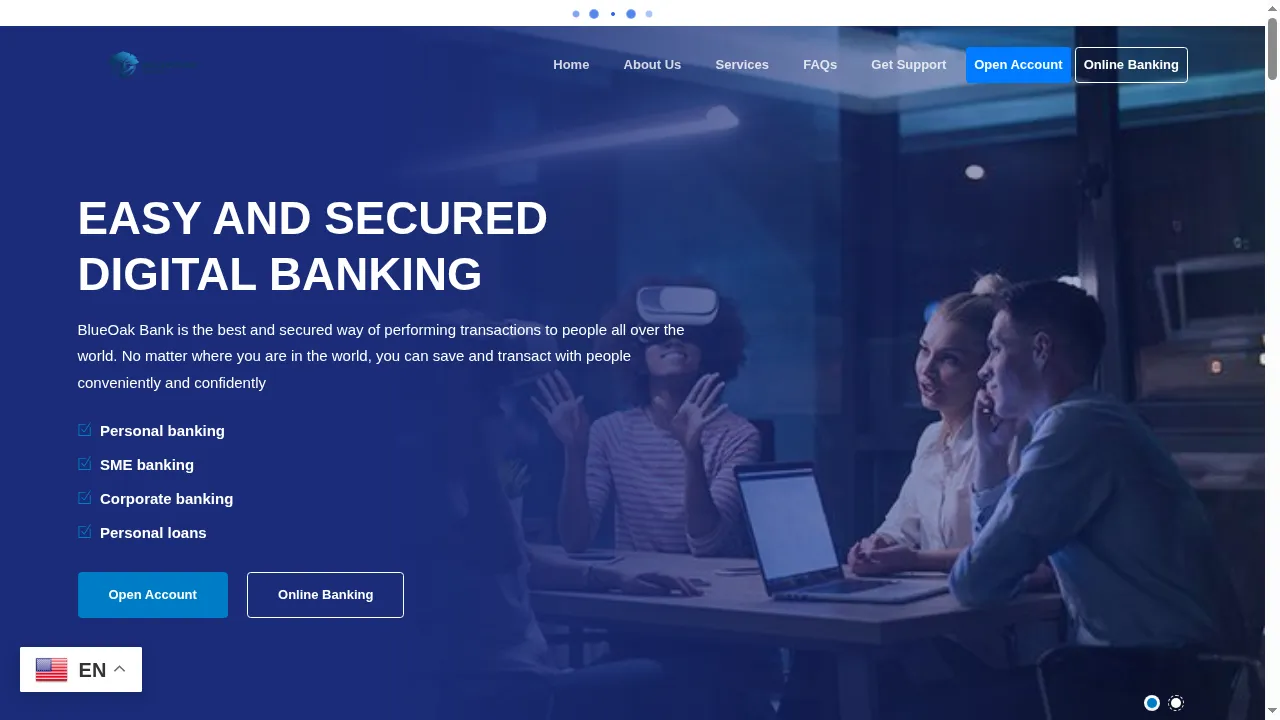
https://blueoakbank.net
Risk score10/10- The domain was registered very recently, which is a common indicator of fraudulent websites set up for short-term scams.
- The site presents itself as a Central Bank-licensed microfinance bank but provides no verifiable regulatory credentials, licensing numbers, or links to official financial regulator databases.
Miễn trừ trách nhiệm: Chúng tôi không đảm bảo kết quả chính xác và không chịu trách nhiệm cho bất cứ điều gì.